CNP fraud WooCommerce can look like a normal order until small amounts, new delivery addresses, repeated attempts, or other details line up.
The consequences can include chargebacks, shipped goods, processor costs, and exposed payment data. Strong WordPress security helps protect checkout from compromise, while gateway controls address payment fraud.
By the end of this guide, you’ll know how to spot the signals, match each risk to the right control, and respond without blocking every unusual order.
TL;DR: Use your payment gateway’s fraud checks and authentication features, add a reputable WordPress security plugin, slow repeated checkout attempts, and review unusual orders before shipping. Follow WooCommerce security best practices to keep WordPress, WooCommerce, plugins, and custom checkout code updated and secure so attackers cannot skim payment data or manipulate checkout.
What does CNP fraud look like
Card-not-present (CNP) fraud is a transaction made without the physical payment card being present. Online purchases, phone orders, mail orders, and recurring payments all fit that definition. In WooCommerce, a thief can use a legitimate checkout with stolen card details, so the order may look normal at first.
Separate the problem into two paths. Payment fraud means someone uses stolen card details and the payment gateway must evaluate the transaction while you decide whether to fulfill it. Checkout or site compromise includes WooCommerce security issues such as payment skimming, compromised administrator accounts, or unauthorized changes to checkout code. The site-security layer and the host must help contain that risk.
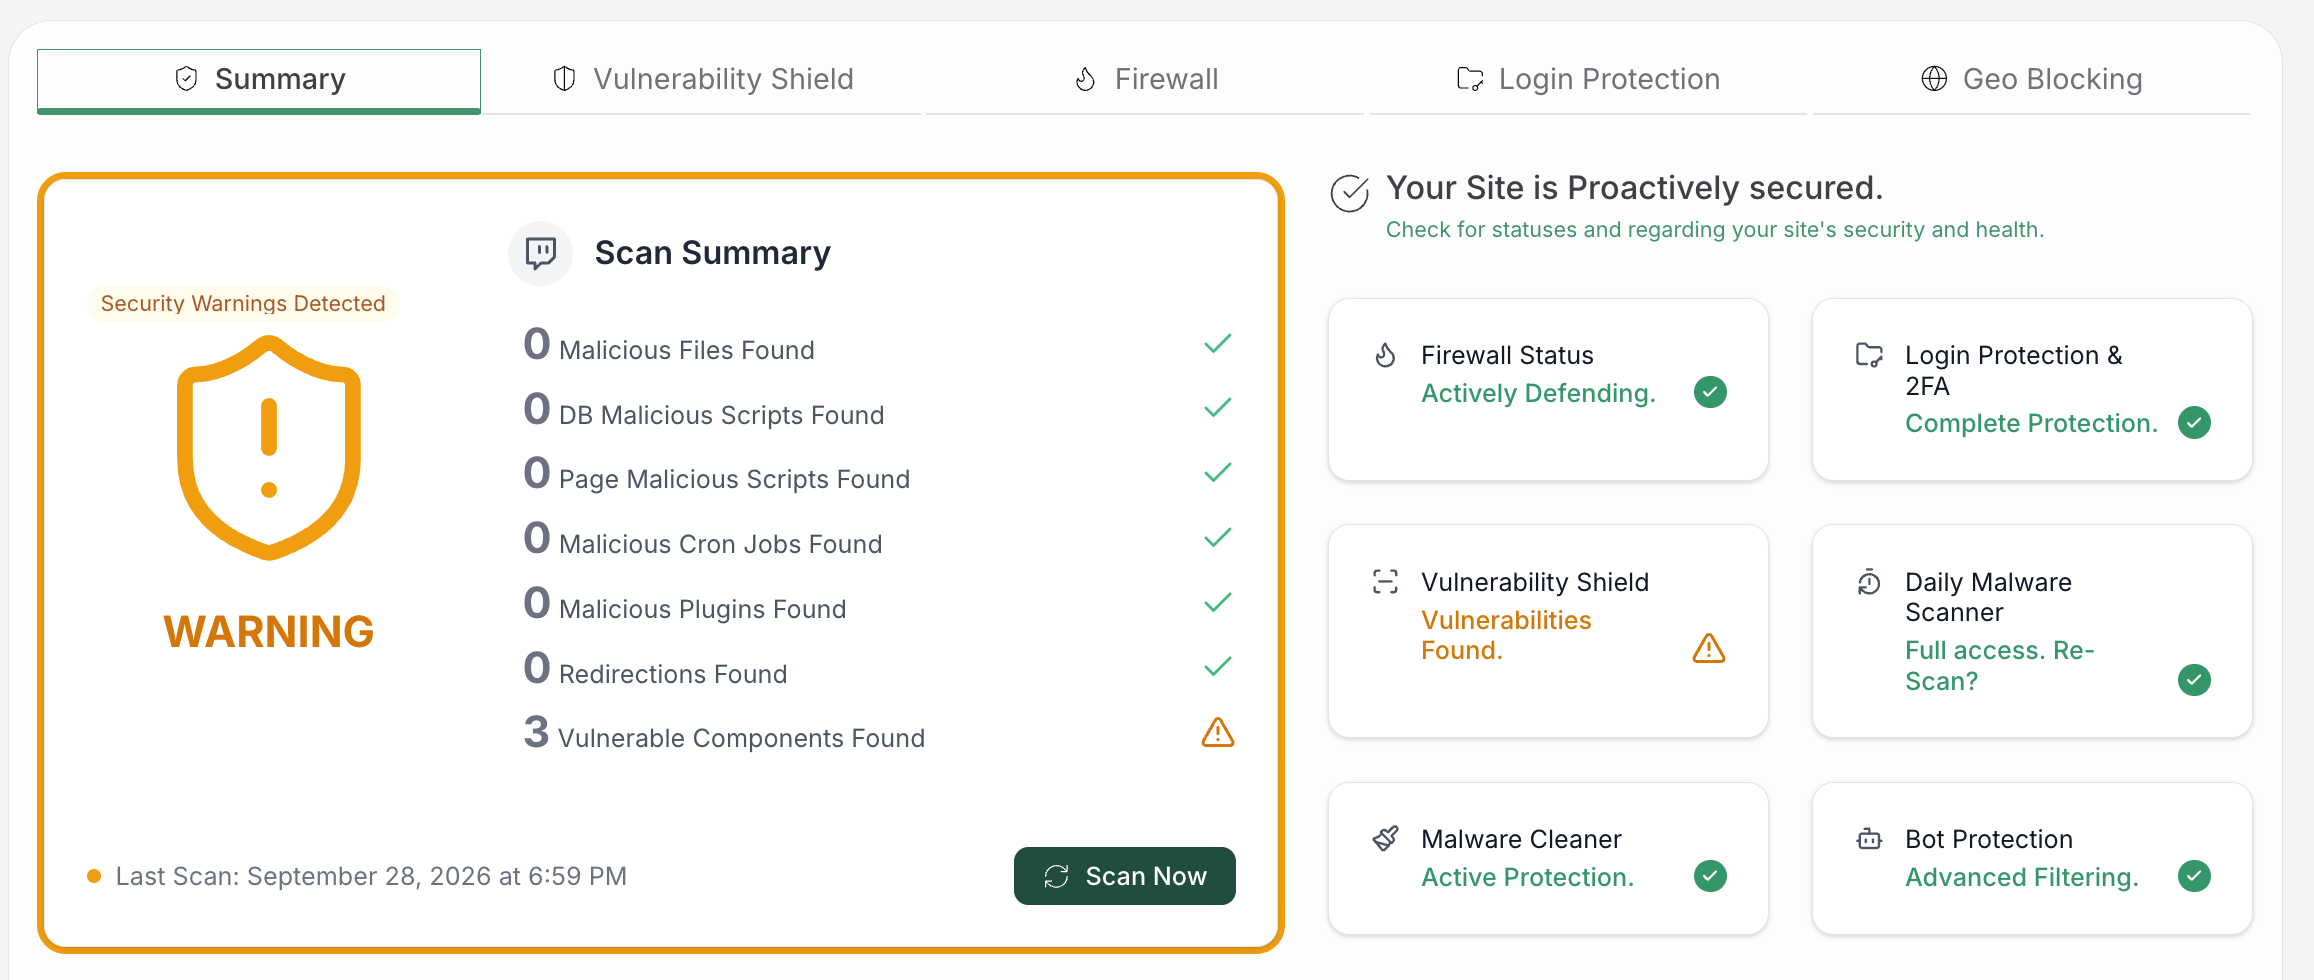
These paths can overlap, though they need different controls. A successful authorization, the gateway’s acceptance of a payment request, does not prove that the buyer is the cardholder. A WordPress firewall does not decide whether a payment is authorized. Treating both risks as one problem leaves a gap somewhere.
📝 Note: A chargeback can still follow a successful authorization and shipment, so the payment result is one piece of the decision.
The signals should you check
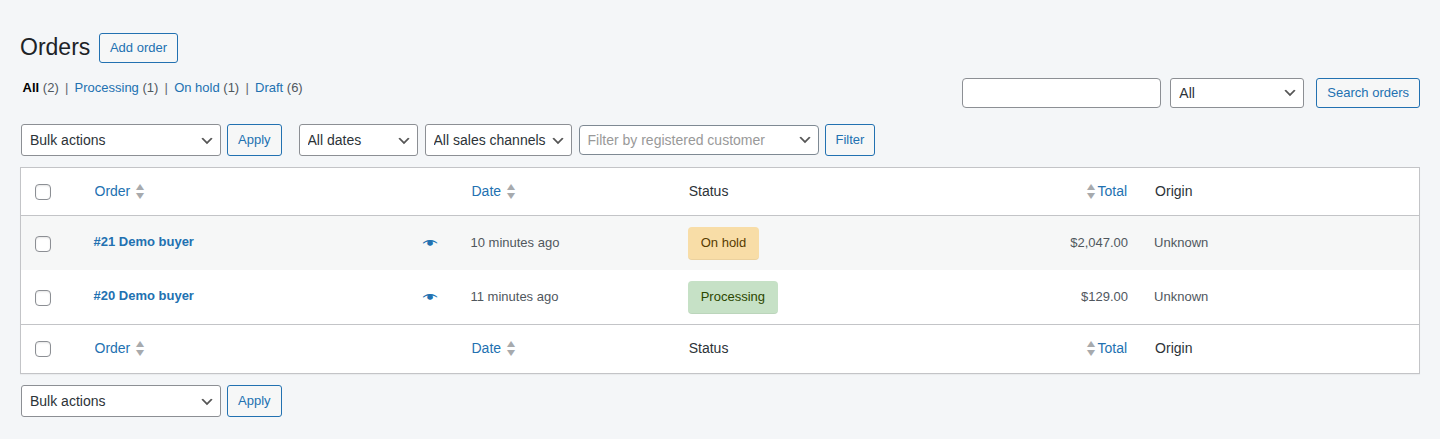
Several signals together matter more than one warning. A billing and shipping mismatch can be normal for a gift; an IP address, which identifies a network connection, can belong to a shared office, mobile carrier, or VPN, and a high-value order can be genuine.
- Compare the order with its destination. A country, currency, phone number, or delivery location that falls outside your usual customer base deserves a closer look. A new or unusual shipping address adds context to a billing and shipping mismatch.
- Look for repeated attempts. Several attempts tied to one IP address, email address, device, payment identifier, or other checkout detail can point to abuse. The same card or session producing repeated declines followed by a successful payment is another reason to pause.If these attempts are also creating suspicious orders, check how to prevent fake orders on WooCommerce alongside your gateway’s fraud controls.
- Check the size and urgency. An unusually high value, quantity, or resale-friendly product mix can raise risk. So can urgent shipping or a request to change the delivery address after the order was placed.
- Watch the customer and the connection. Disposable email, inconsistent phone details, avoidance of ordinary verification questions, or VPN and anonymizer traffic alongside repeated payment attempts all add context. An unfamiliar login, password reset, address change, or sudden purchase can signal trouble in a customer’s account.
- Read the gateway record beside the WooCommerce order. Check the authorization result, AVS, which compares billing and address details, CVV, which checks the card security code, authentication status, previous orders, and the timing of attempts when the gateway provides those records.
These signals can raise or lower risk without proving that a customer is legitimate or fraudulent.
📝 Note: A shared network can connect many genuine shoppers, so a broad IP block may create more harm than the original burst of attempts.
Which fraud path is unfolding
Knowing the attack pattern helps you choose a response instead of applying the same block to every order. Once the signals show which path may be unfolding, use the matching response below.
Block card testing carefully
WooCommerce card testing attacks involve bursts of small payment attempts used to find stolen card numbers that still work. An attacker may create many failed orders, vary billing details, or spread attempts across accounts and IP addresses.
Even declined attempts can create processor noise, gateway fees, support work, and a warning from the payment provider. Check failed orders and payment logs, then consider gateway velocity controls, which limit attempts over a period, and CAPTCHA.
CAPTCHA asks a visitor to complete an anti-bot challenge. Use rate limits that restrict repeated requests and rules for repeated failures, and ensure that CAPTCHA works with the actual checkout.
Avoid blocking a whole country or broad IP range unless the evidence supports it; keep in mind that shared networks can include legitimate shoppers.
📝 Note: Card testing is an attack pattern at checkout, while a chargeback is a later payment dispute. They require different records and response steps.
Protect checkout from skimming
A checkout skimming attack happens when malicious code captures payment information during checkout. The code, including malware or other malicious software, may enter through WordPress, a plugin, a theme, a compromised administrator account, or a third-party checkout integration.
Treat possible skimming as a security incident because customers can be exposed even when their payments appear to succeed. Keep software updated, limit administrator privileges, use secure credentials and backups, run a firewall and malware scans, and check unexpected changes to checkout code.
If compromise is possible, preserve evidence, involve the host and security provider, and contact the gateway for advice on exposure and payment handling. An ordinary order review cannot contain this path.
📝 Note: A clean-looking order does not show that checkout code stayed clean during the payment.
Check phishing and account takeover
Phishing can expose a customer’s login or payment details before they reach the store. An account takeover can then produce a familiar-looking purchase because the account, shipping address, and order history appear normal.
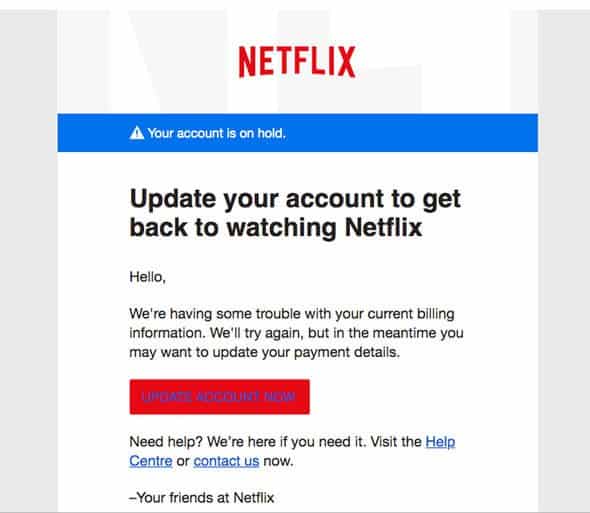
Check unusual logins, password resets, address changes, and sudden changes in order behavior. Protect administrator accounts with strong unique passwords and two-factor authentication where available. Customers may need to reauthenticate or confirm unusual changes when the account and gateway support that workflow.
Prepare for refunds and chargebacks
A chargeback is a payment dispute raised after a transaction. It differs from card testing, which happens through repeated attempts at checkout. A chargeback can arrive after a successful authorization and shipment.
Keep order, delivery, customer communication, and gateway evidence according to the gateway’s dispute process. The gateway’s dispute tools and deadlines determine the response. No checkout rule or site-security layer can eliminate chargebacks.
How do you prevent CNP fraud WooCommerce?
Once you identify the path, give each layer a defined job. Payment controls evaluate the transaction, checkout controls slow abuse, human review handles ambiguity, and site security protects the code.
Configure the payment gateway
Start with the payment gateway, the service that processes the payment request, because it sees payment and authentication data that WordPress does not. Enable the fraud checks and authentication options it supports, such as AVS, CVV verification, 3-D Secure, risk scoring, velocity checks, and dispute tools.
Names, response codes, liability rules, and availability differ by gateway and region. Confirm the current controls in the gateway’s documentation before changing them.
Set higher-risk orders to review or hold instead of automatically fulfilling them. Staff should know which gateway outcomes permit shipment, which require customer verification, and which should be canceled. A fraud score, a gateway’s estimate of transaction risk, is a decision aid. CVV, AVS, and 3-D Secure can reduce some risks without proving that the buyer is the cardholder or preventing every dispute.
📝 Note: The gateway’s actual response codes and policy matter more than the label of a fraud feature.
Slow repeated checkout attempts
Add controls for bots and card testing at the checkout surface. Depending on the gateway, WooCommerce setup, and extension support, these may include CAPTCHA, rate limiting, order-velocity rules, failed-attempt thresholds, and allow or block lists.
If your setup needs an extension, compare WooCommerce fraud prevention plugins against your gateway and checkout requirements.
Start in observe or review mode when possible. Compare the results with your order history before enabling automatic blocking. A narrow rule can stop future attempts, while a shared IP can also affect real customers. Reserve allow rules for known-good cases and review them over time.
Feature names such as Fraud Prevention, Anti-Fraud, and Anti-Fraud Protection are not interchangeable. Availability can depend on the hosting platform, checkout type, extension, or gateway, so do not assume that a control exists in every WooCommerce store.
📝 Note: CAPTCHA can reduce automated attempts while adding checkout friction, which makes testing on your actual checkout important.
Review unusual orders before fulfillment
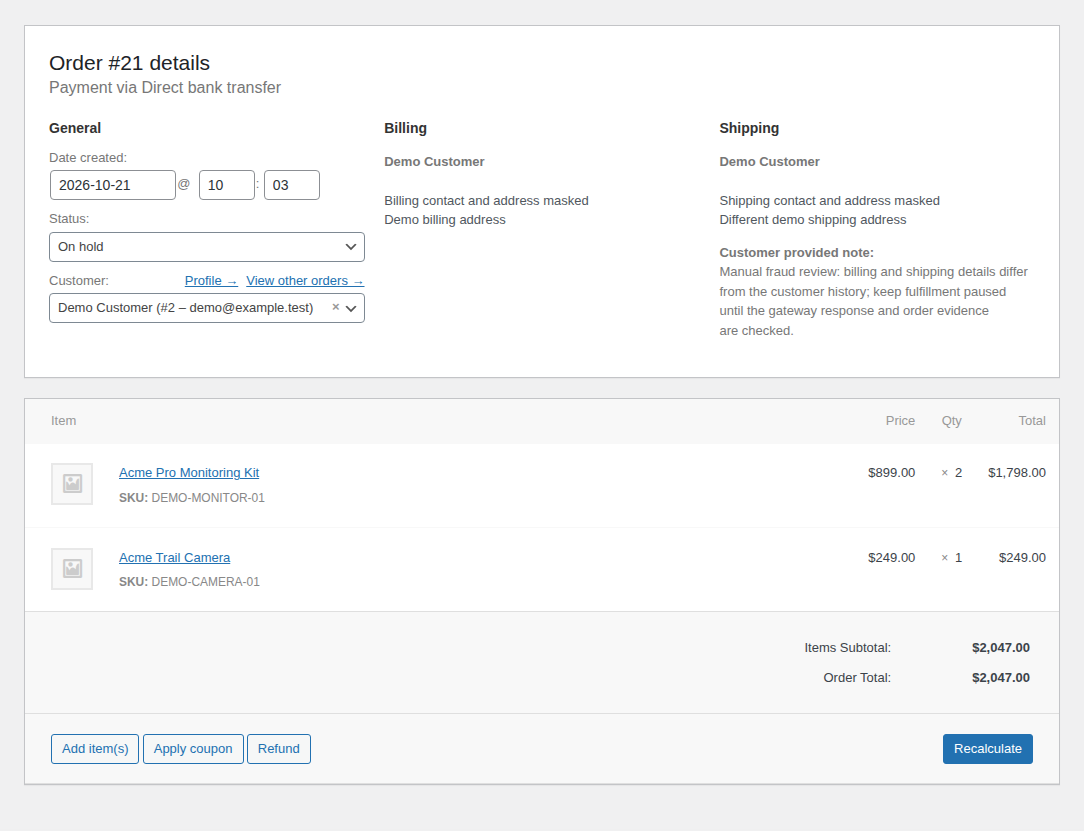
Create a short checklist for staff before an unusual order ships. Compare the order with prior behavior, inspect gateway results, confirm shipping details, and review the timing and pattern of recent attempts.
If risk remains unclear, pause fulfillment and use a verification process that does not ask for sensitive card data by email. Authorization alone should not make a suspicious order easier to approve. A mismatch alone should not cancel every order either.
Record the reason for each decision since those records help you tune rules around real false positives and confirmed fraud. A consistent review record turns individual judgment calls into evidence for safer future rules.
Keep WordPress and checkout clean
Apply WordPress security updates promptly, and keep WooCommerce, plugins, themes, and checkout integrations updated. Remove software that is no longer needed. Restrict administrator access, use unique credentials, enable multi-factor authentication where available, and keep tested backups.
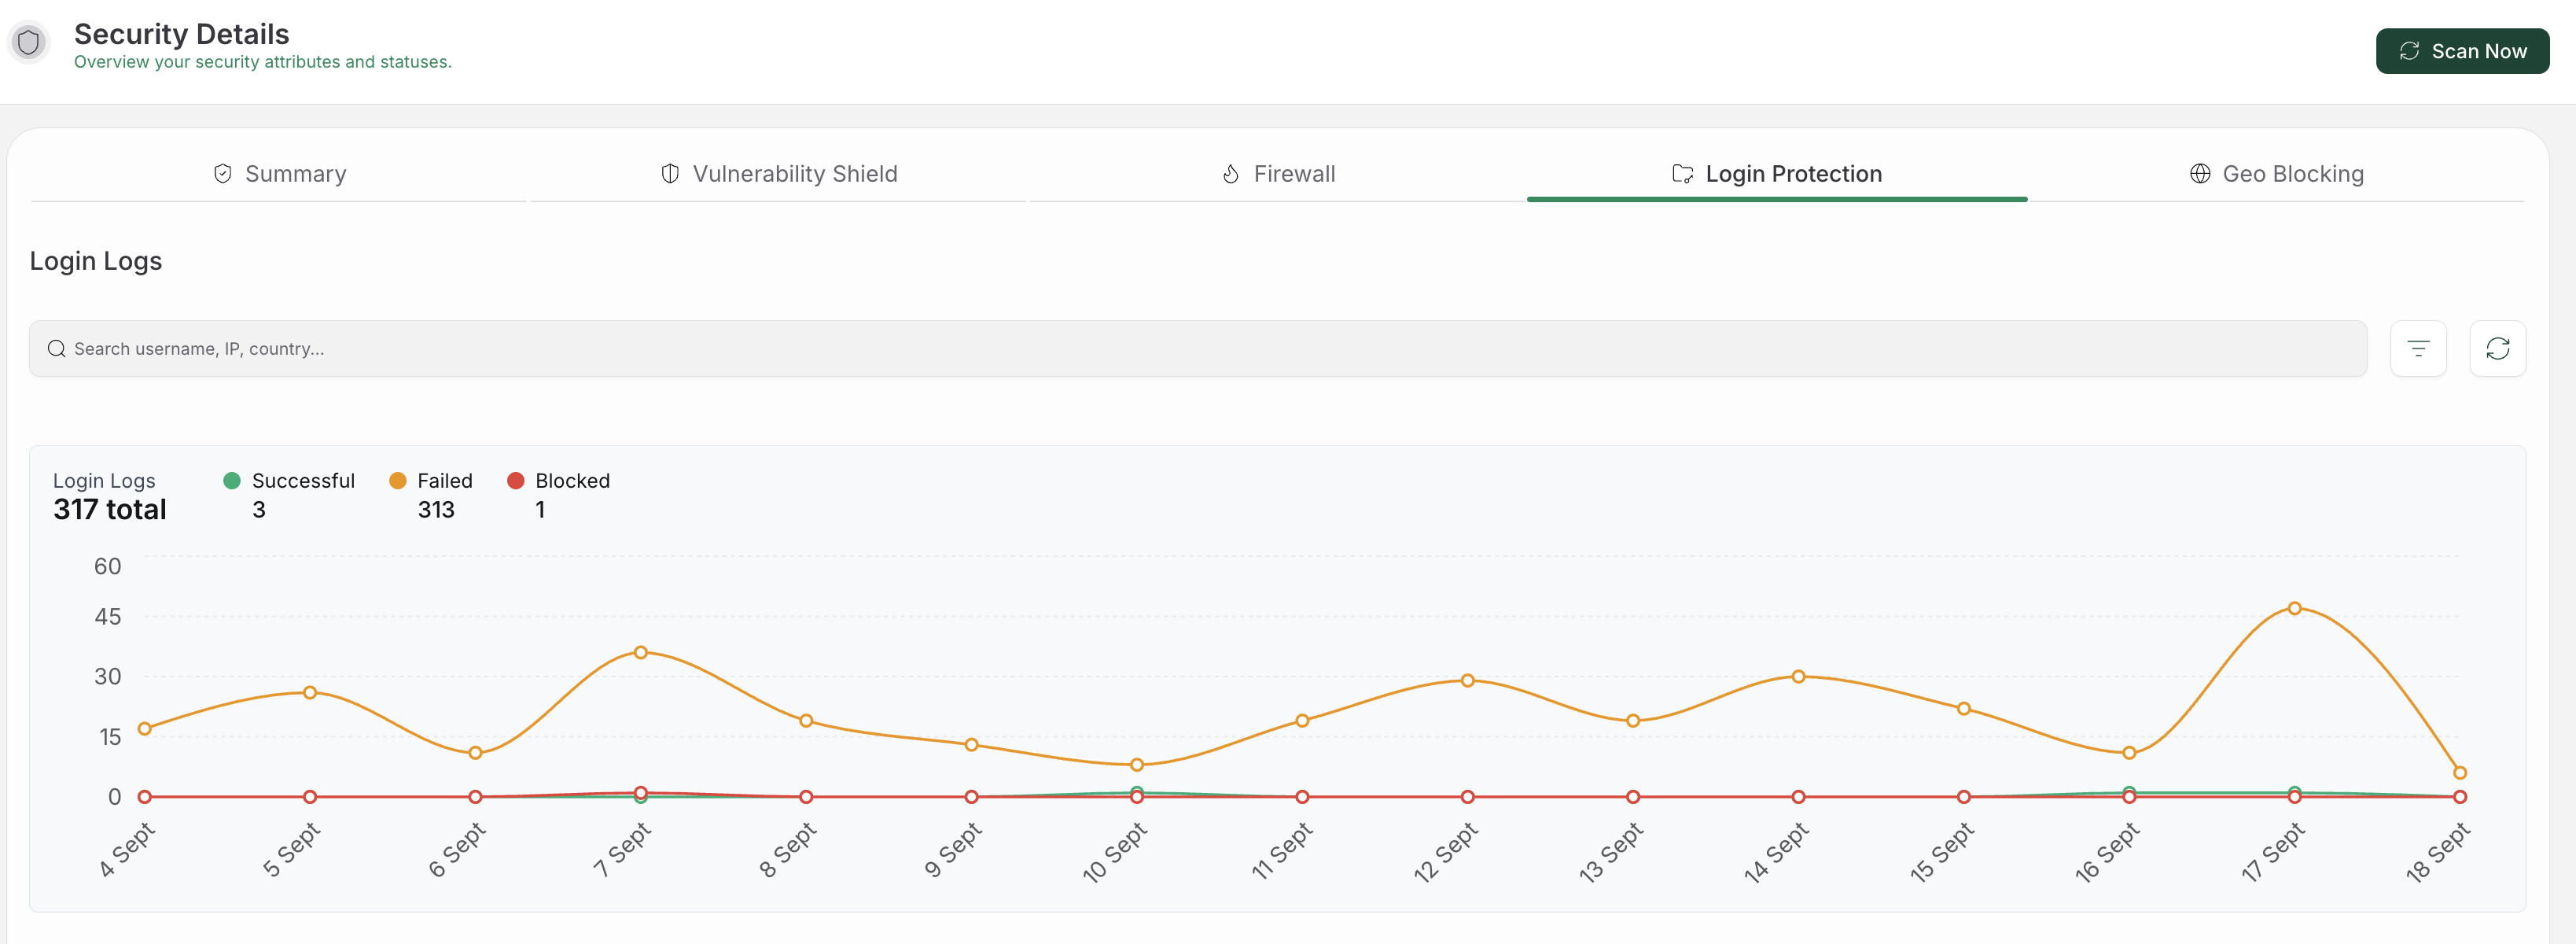
When choosing a tool, compare WooCommerce security plugins for malware scanning, cleanup, firewall protection, and login security.
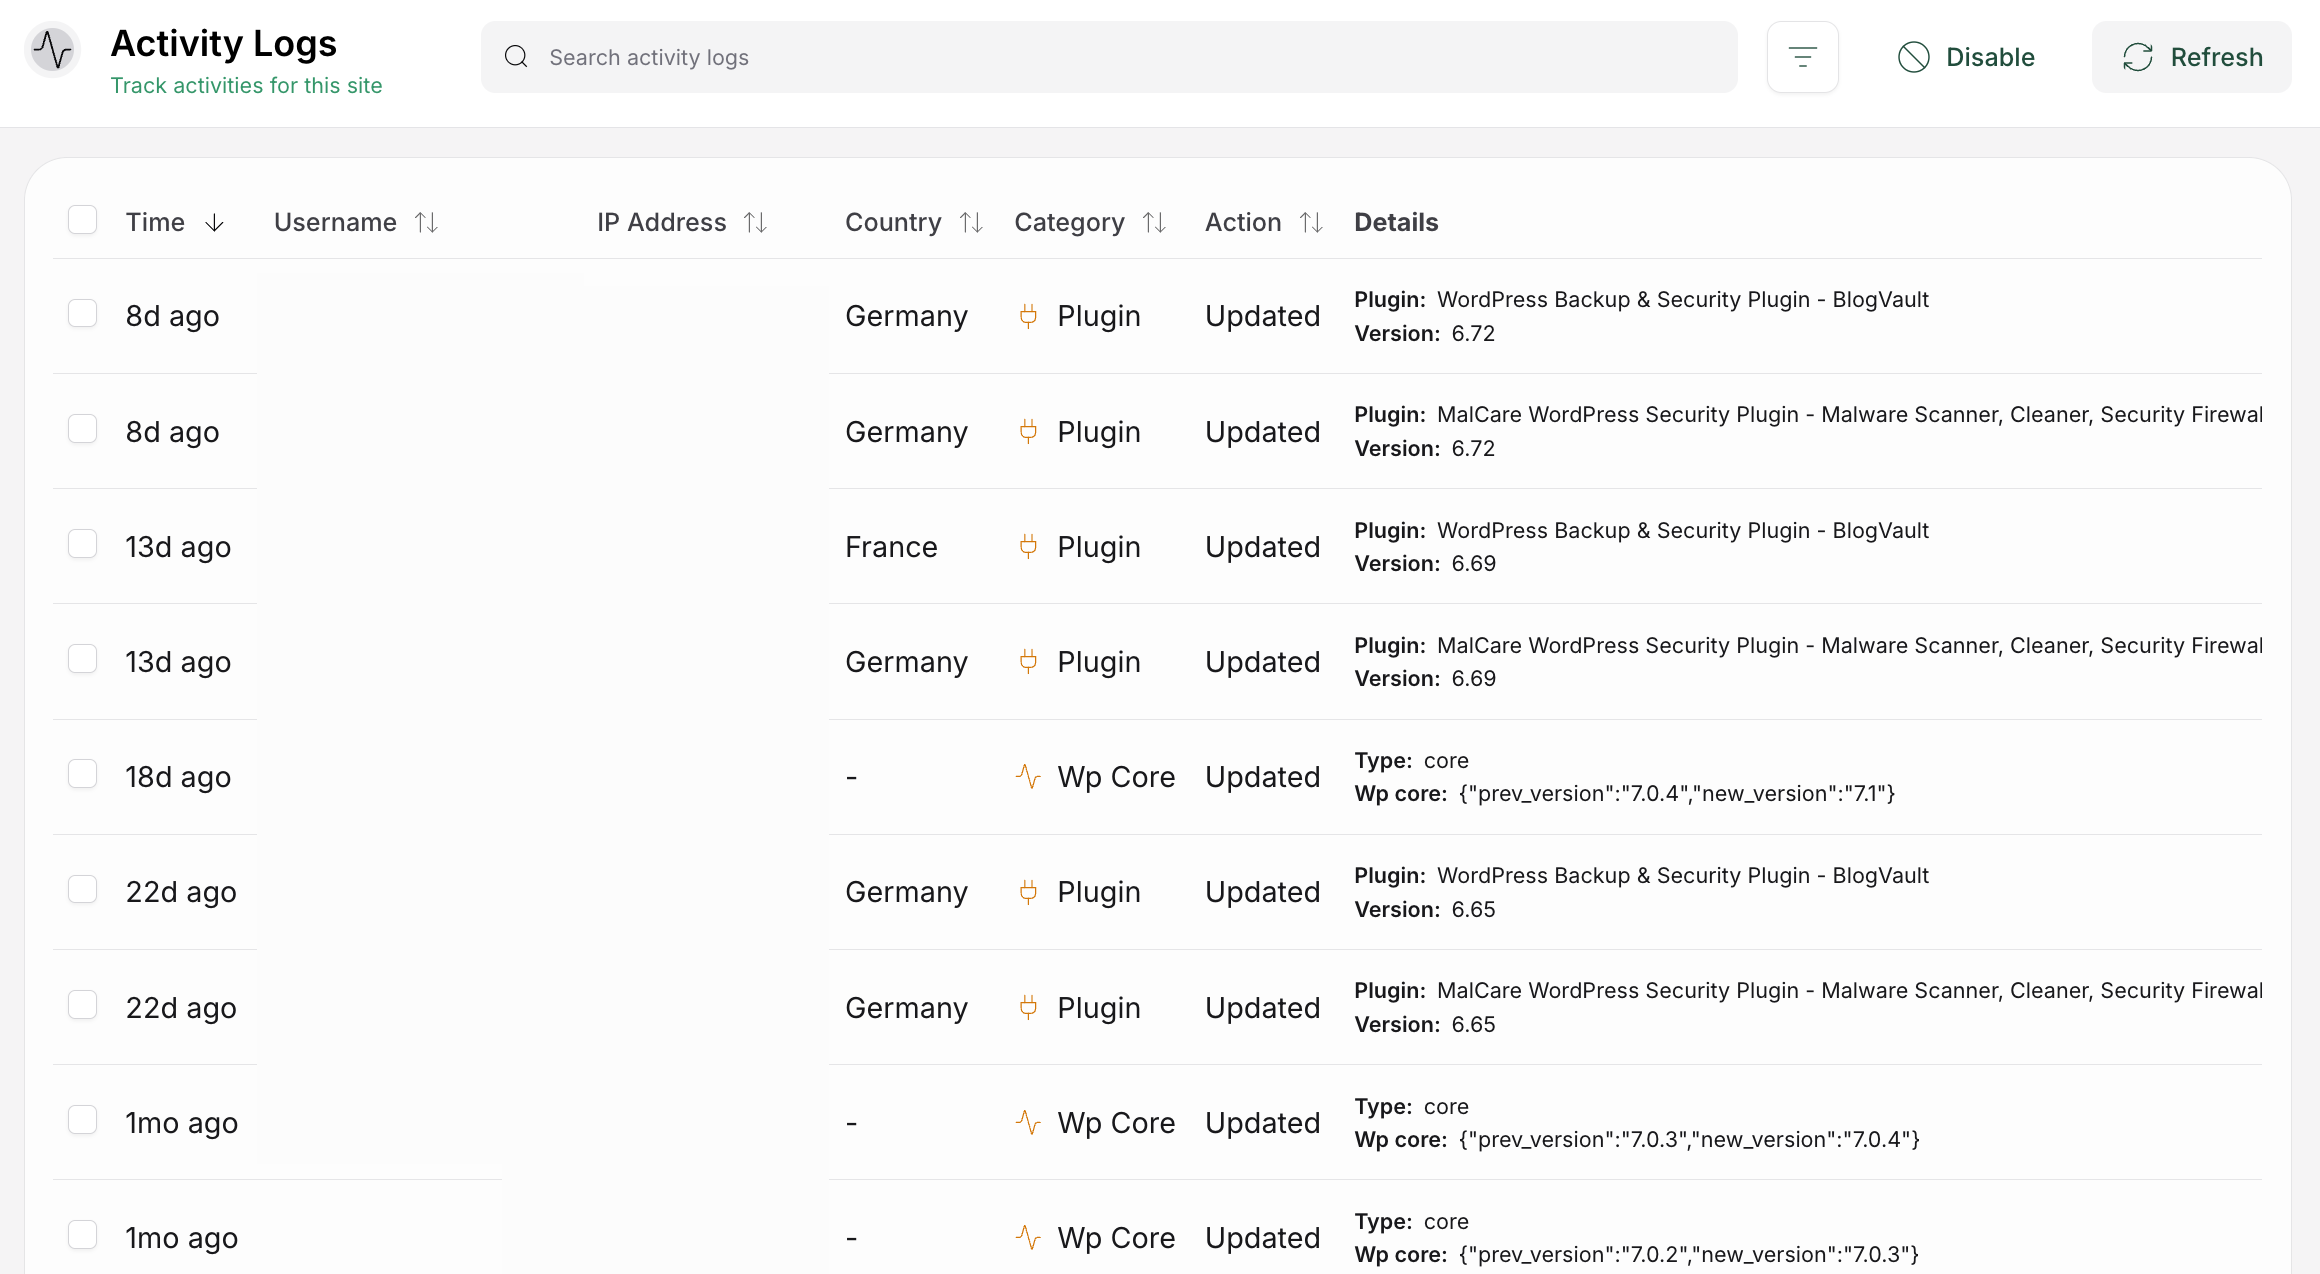
Review unexpected changes to checkout files, payment scripts, administrator accounts, and plugin settings. Use a WordPress activity log to trace recorded logins, user changes, and plugin activity during your investigation. MalCare’s firewall can reduce malicious requests and help detect or respond to malware or skimming risk. It does not provide AVS or CVV checks, authorize payments, calculate the gateway’s fraud score, manage chargebacks, or replace manual order review.
The payment and site-security layers work together. Keep their jobs separate so a site-security alert does not become a false payment decision.
📝 Note: A security layer protects the checkout surface, while the payment layer evaluates whether a transaction should proceed.
Decide carefully about guest checkout
Disabling guest checkout can add an account and identity signal, though it also adds friction. Customers may abandon the purchase, and attackers can still create accounts or use compromised accounts.
Treat guest checkout as one optional control in a wider risk strategy. It does not stop every bot or stolen-card order, so weigh its conversion impact against the evidence from your own store. Requiring an account changes the customer journey without proving that the new account belongs to the cardholder.
What should you do after a suspicious order
First, pause fulfillment for the affected orders. Do not delete the orders or payment records. Save the order details, gateway response, timestamps, delivery information, customer communication, and related failed attempts according to your privacy and retention policies.
- For one unusual order, place it on hold and follow the store’s verification process. For a burst of payment attempts, check gateway and server logs, apply a narrow temporary control and contact the gateway if the activity continues.
- For suspected skimming, malware, or administrator takeover, restrict access as safely as possible. Contact the host and security provider, scan and investigate the site, and ask the gateway what customer or payment steps are required.
- For a chargeback, use the gateway’s dispute workflow before its deadline. Submit the requested order, delivery, authorization, and communication evidence.
After containment, check the root cause. Follow a WordPress security audit to review software, account access, and remaining security gaps before closing the incident. Review administrator logins, plugin and theme changes, checkout scripts, web-server logs, payment settings, and recent user or address changes.
Restore only from a trusted backup and change affected credentials. If customer payment data may have been exposed, follow the gateway’s incident process and the legal or regulatory requirements that apply to the business.
📝 Note: Preserving the original records gives the host, gateway, and security provider a shared timeline to investigate.
How should you tune fraud rules
Start with your store’s normal pattern. Record typical order value, products, locations, delivery methods, customer types, and order velocity before setting hard blocks. A rule that fits a high-value international store may harm a local store with many first-time buyers.
Use review thresholds before hard blocks. Check how many good orders would have been stopped, how many confirmed fraud attempts would have passed, and whether a rule affects shared IP addresses, mobile networks, or legitimate VPN users. Raise or lower weights and velocity limits gradually, and review any allowlist, a list of accepted cases, instead of treating it as permanent trust.
The goal is to make risky combinations harder to complete while keeping a clear path for a legitimate customer who needs help. Recheck the rules after promotions, new shipping regions, gateway changes, and major changes to the product catalog.
📝 Note: A rule that performs well during an ordinary week may behave differently during a promotion or a change in shipping geography.
FAQs
Does a firewall prevent CNP fraud
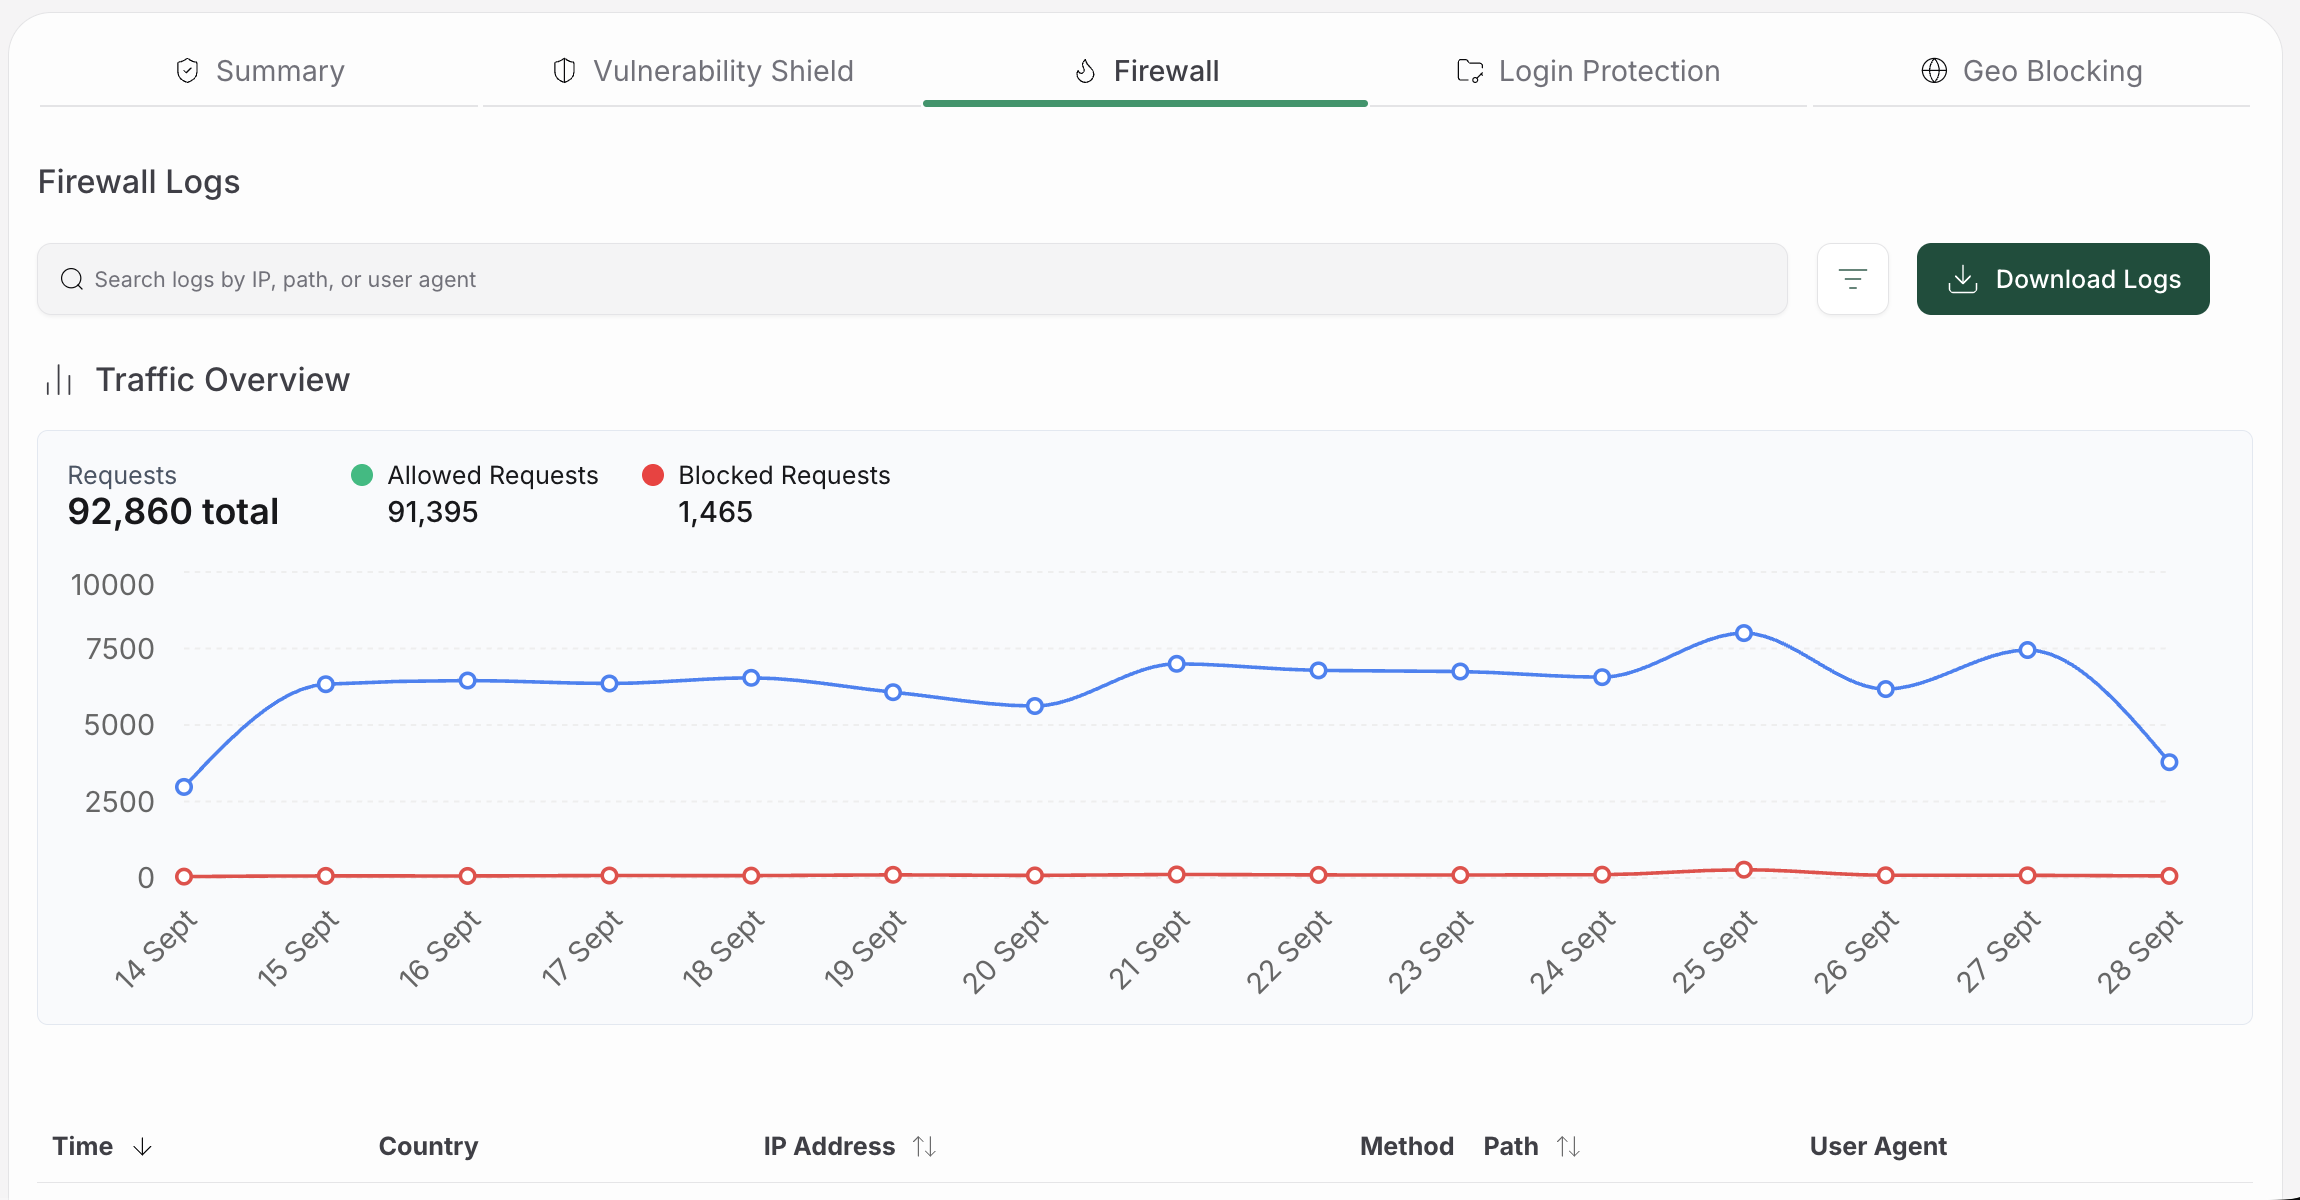
No. A firewall can reduce malicious requests and help protect or investigate a compromised WordPress checkout. It does not authorize a card, run AVS or CVV checks, provide 3-D Secure, calculate a payment risk score, or handle a chargeback. Use it with gateway controls and order review.
Should I disable guest checkout to stop CNP fraud
No, guest checkout is not a standalone solution. Disabling it may add an identity signal, though it also adds friction and does not stop bots, stolen card details, or account takeovers. Test the conversion impact and use it as one part of a layered fraud-control policy.
Does a successful authorization prove an order is safe
No. Authorization means the gateway accepted the payment request under its rules. It does not prove that the buyer is the cardholder or that the order will avoid a chargeback. Review unusual orders before shipping and keep the gateway’s response and fulfillment evidence.
What is the difference between card testing and a chargeback
Card testing is an attack pattern involving repeated payment attempts, often to identify usable stolen cards. A chargeback is a later dispute raised through the payment network after a transaction. Card testing calls for checkout and gateway controls; a chargeback calls for the gateway’s dispute process and supporting evidence.
What is the first step after suspected checkout skimming
Pause affected fulfillment and preserve the relevant order, gateway, access, and server records. Contact the payment gateway, host, and security provider, then investigate the checkout and administrator accounts. Do not treat suspected skimming as an ordinary bad-order block because customers may have been exposed.
Conclusion
You do not need every order to look the same before you can protect your store. Match gateway checks, checkout controls, human review, and site security to the risk in front of you. When the next odd batch appears, keep a record, choose a narrow response, and follow the clearest next step. Review your fraud rules regularly as your products, customers, payment gateway, and shipping regions change.
Use a reputable WordPress security plugin alongside gateway protections to help secure checkout and detect suspicious site activity. With layered controls and a consistent review process, you can reduce fraudulent orders without creating unnecessary barriers for legitimate customers.