Your payment form works, visitors are completing their purchases, donations, or bookings, and nothing in your dashboard hints at trouble until your payment processor writes to say that fraudulent charges keep tracing back to cards used on your site.
That is what a skimming attack looks like from the owner’s side: a site that behaves perfectly while a few lines of hidden code copy whatever visitors type into a payment form.
For online stores, protecting checkout is a critical part of WooCommerce security, even when payments appear to work normally. This guide covers how to check whether that is happening to you, what to do in the first hour if it is, and how to keep it from coming back.
TL;DR: A skimming attack is hidden code that copies card details while visitors type them into a payment form, and the payment still goes through, so a normal-looking site proves nothing. If you suspect one, pause the payment page, save the evidence, scan the whole site (files and database), remove the malware and any backdoor, and change every password and key, then tell your host and payment processor.
Find your situation
| Where you are right now | Where to go |
|---|---|
| Customers, donors, your processor, or your bank report fraud | What to do in the first hour |
| Your host, Google, or a security tool warned you | Signs of a skimming attack |
| Nothing has gone wrong, and you want to know if you’re exposed | How a skimmer reaches a WordPress site, then prevention |
What a skimming attack is
In an online skimming attack, malicious code copies payment details while a visitor types them into a payment form, and the payment still goes through. You’ll also see it called web skimming, e-skimming, formjacking, or Magecart.
Europol describes these attacks as stealing payment information during checkout, often without anyone noticing. What gets copied depends on what the infected page can read, which usually includes card numbers, CVV codes, and billing details.
Skimming is not:
- A device on an ATM or card reader. That is the physical version, and it needs hardware.
- Something only online stores face. Any WordPress page where visitors type card details, including donation and booking forms, can be targeted.
- Something HTTPS stops. HTTPS protects data on its way to your server, while the skimmer runs in the visitor’s browser.
- The same as WooCommerce card testing attacks. Card testing uses repeated payment attempts to check whether stolen cards still work; skimming copies card details as visitors enter them.
How a skimmer reaches a WordPress site
Skimmers usually get in through a breach, get their code into the payment page, then collect what visitors submit. Europol describes the same three stages: breach, inject, and collect.
For store owners, skimming is one of several WooCommerce security issues that can put checkout and customer data at risk.
These are the routes that public reports describe:
- A vulnerable plugin on the payment page. In May 2026, Sansec reported that attackers were exploiting Funnel Builder by FunnelKit, a checkout plugin on more than 40,000 WooCommerce stores (CVE-2026-47100). Versions before 3.15.0.3 let unauthenticated attackers plant a script in the plugin’s External Scripts setting, which then loaded on checkout pages. The planted code posed as Google Tag Manager.
- A widget or database entry. In January 2025, Sucuri described a skimmer hidden in the wp_options table, in a row called widget_block, and inserted through a Custom HTML widget. It activated only on pages whose address contained “checkout.”
- A compromised plugin download. In July 2025, Patchstack reported that two Gravity Forms versions offered for manual download contained a backdoor. It was not a skimmer, but a backdoor gives an attacker a foothold on the site.
Signs of a skimming attack
Most skimmed sites show no sign at all, so the first report usually comes from outside your dashboard.
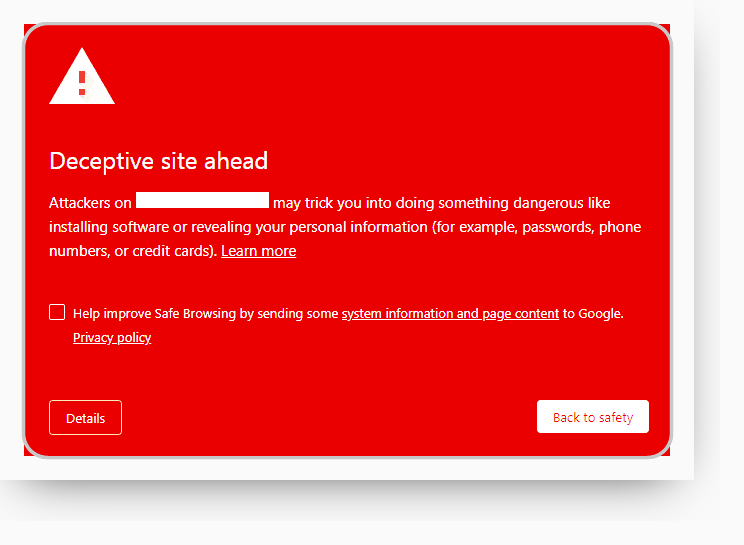
Watch for these signals, and treat more than one together as a strong reason to investigate:
- Fraud reports from customers, donors, or card issuers after payments on your site
- Alerts from your payment processor or acquirer
- Warnings from your host, Google, or browsers
- Unexplained changes to a payment page script, plugin or theme file, script setting, tag manager container, plugin list, or administrator accounts
- A Custom HTML widget containing a script tag, which is where the January 2025 skimmer was placed
- An unfamiliar domain in your payment page’s network requests, or a live connection to another server opening while card details are typed
Fraudulent orders alone don’t prove that your site contains a skimmer. Card-not-present fraud can also involve card details stolen elsewhere.
You can check the network requests yourself. Open your payment page in a private window while logged out, open your browser’s developer tools, go to the Network tab, reload, and look at which domains it contacts. Use your gateway’s test card numbers, never real cards.
What to do in the first hour
If customers or your processor report fraud, treat it as an incident until you can show otherwise.
Pause the payment page, or the whole site if you can’t isolate it. Keep the site reachable for yourself and your host, and write down when you paused it, what you saw, and who made the change.
Save logs, suspicious files, and screenshots before you delete anything. Removing the first odd file can erase the trail to the entry point.
Check the usual hiding places before a full cleanup. These include plugin settings that accept scripts, Custom HTML widgets under Appearance > Widgets, header and footer script settings, your tag manager container, theme files such as functions.php, the mu-plugins folder, unfamiliar plugins, and administrator accounts you didn’t create.
Tell your host and payment processor what you found and when. They can help with logs and card-brand steps. Notification duties to customers vary by country and contract, so ask a privacy or legal adviser.
📝 Note: Test with your gateway’s test mode, never with real card data.
How to remove a skimmer and recover
- Scan the whole site, files, and database, not only the payment page. A skimmer can sit in a plugin, a theme file, a database entry, or a setting.
- Remove the infection along with any backdoor. A backdoor is a hidden way back in, and it can be a file, an administrator account, or a scheduled task. Clearing only the first thing you noticed is how infections return.
- Close the entry point. Update the vulnerable plugin or theme, and delete plugins you no longer use.
- Change every password and key once access is removed. That covers WordPress administrators, hosting, the database, SFTP, staff accounts, and payment-gateway keys. Changing them before the backdoor is gone just hands the attacker the new ones.
- Be careful when restoring a backup. A backup taken after the break-in restores the malware with it, so choose the last backup you can confirm was clean.
Scan again and test the payment page with test data, then keep watching for changes over the following weeks.
Where a malware scanner fits
A scanner helps most when you need to know whether hidden malware exists anywhere in your WordPress installation. MalCare’s malware scanner checks files and the database, which matters because some skimmers live in the database.
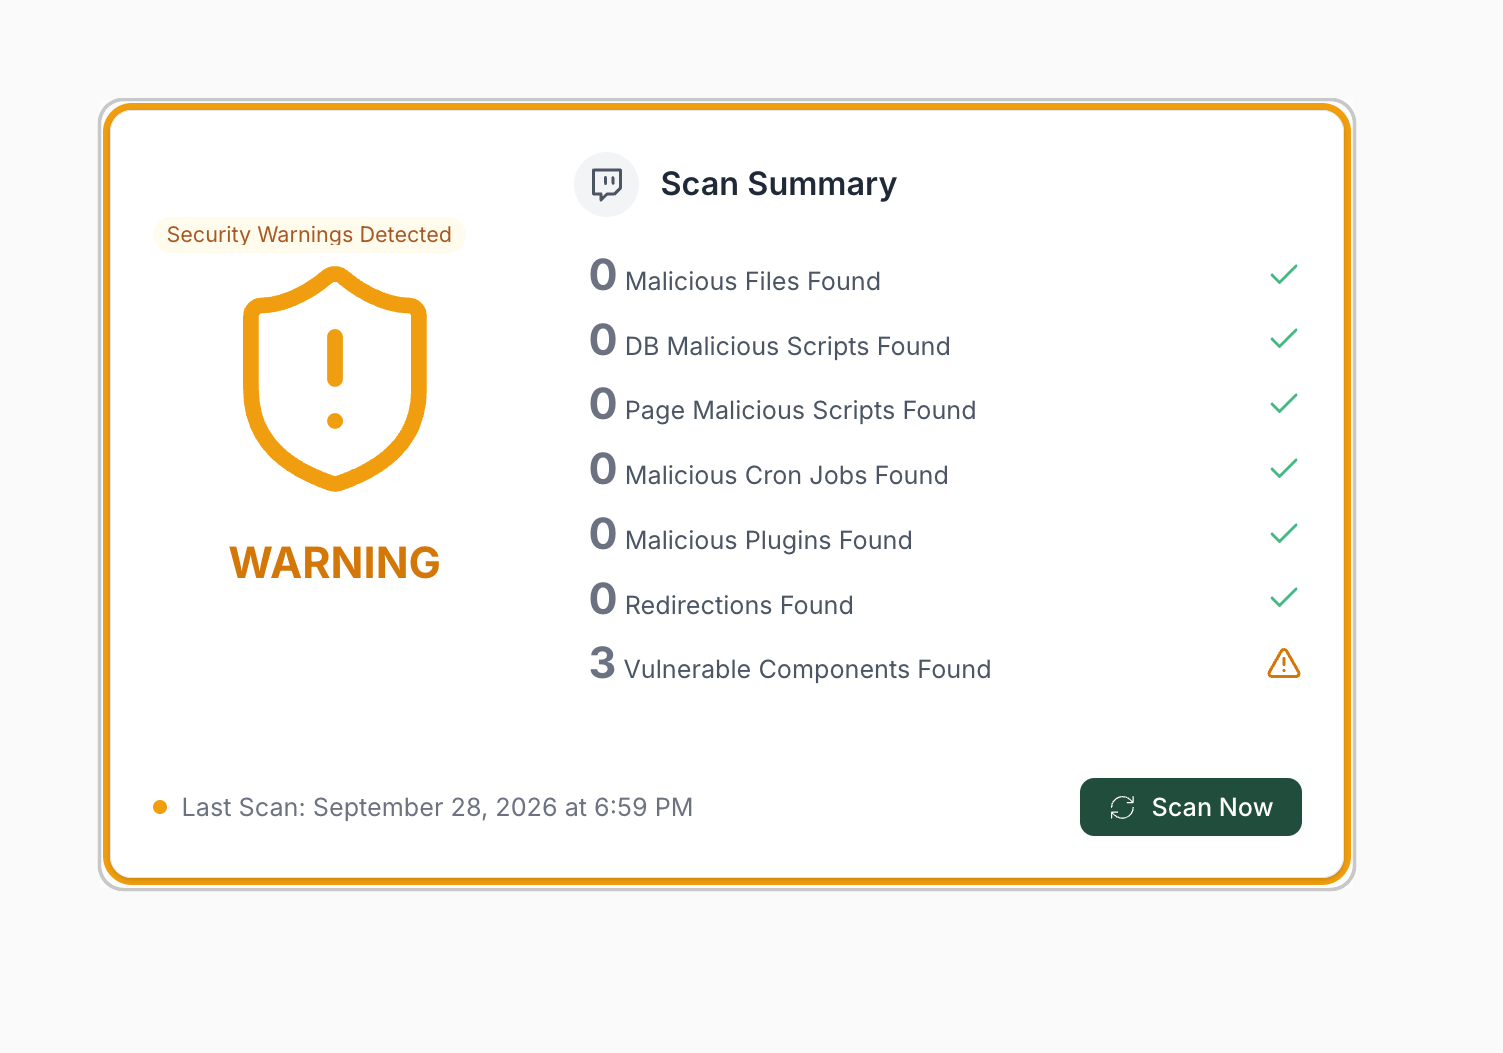
A scan captures one moment. A clean result can’t promise a later compromise won’t happen, and it can’t vouch for scripts that your visitors’ browsers load from other sites, such as a tag manager or a third-party widget.
How to prevent a skimming attack
Good prevention shuts the usual routes in, limits what a skimmer can reach, and catches changes early. If you run an online store, make these steps part of your wider WooCommerce security routine.
Block the ways in
- Keep plugins on the payment path up to date. Known flaws are the routes these reports describe.
- Delete plugins, themes, and snippet plugins you don’t use. Every idle plugin is one more route in.
- Give each person the lowest role they need, and turn on two-factor authentication. Compromised administrator accounts are a common starting point.
- Use a firewall. It can filter harmful traffic while you work through updates.
Limit what a skimmer can reach
- Let your payment provider handle card entry where possible. A hosted card form keeps card fields off your site.
- Keep third-party scripts off payment pages unless you need them. Every extra script is one more thing to verify.
- Consider a Content Security Policy, starting in report-only mode. It tells browsers which sources may load scripts. Test your payment flow before enforcing it.
- Pin fixed external scripts with Subresource Integrity. The browser refuses a pinned script whose contents have changed.
- Turn off the dashboard code editors. Adding
define( 'DISALLOW_FILE_EDIT', true );to wp-config.php removes the theme and plugin editors from the dashboard.
Spot changes early
- Monitor files, plugins, and administrator accounts for unexpected changes.
- Keep a list of every script your payment pages load, and review it on a schedule.
- Check whether PCI DSS requirements 6.4.3 and 11.6.1 apply to you. They cover authorizing and checking payment page scripts and detecting unauthorized changes. Ask your acquirer or a PCI assessor which self-assessment form applies.
FAQs
Does a skimming attack only affect WooCommerce stores?
No. Most documented WordPress cases involve WooCommerce, but any page that collects card details can be targeted.
Does HTTPS prevent a skimming attack?
No. HTTPS protects data in transit, while skimming code runs in the browser.
Does a clean scan prove my site is safe?
No. A scan covers one moment, so it can’t promise a later compromise won’t happen.
Does a hosted payment page make me immune?
It reduces what a skimmer can reach. Attackers can still tamper with the page that links to it.
Do I have to tell my customers?
It depends on your country, your contracts, and the data involved. Ask a privacy or legal adviser.
Conclusion
A site that looks healthy can still be copying cards, which is why a processor’s email often arrives before any warning from your own dashboard. Pause the payment page, save the evidence, scan files and the database, remove any backdoor along with the malware, and change every credential.
Start today by checking your payment page’s network requests and your plugin and widget lists.