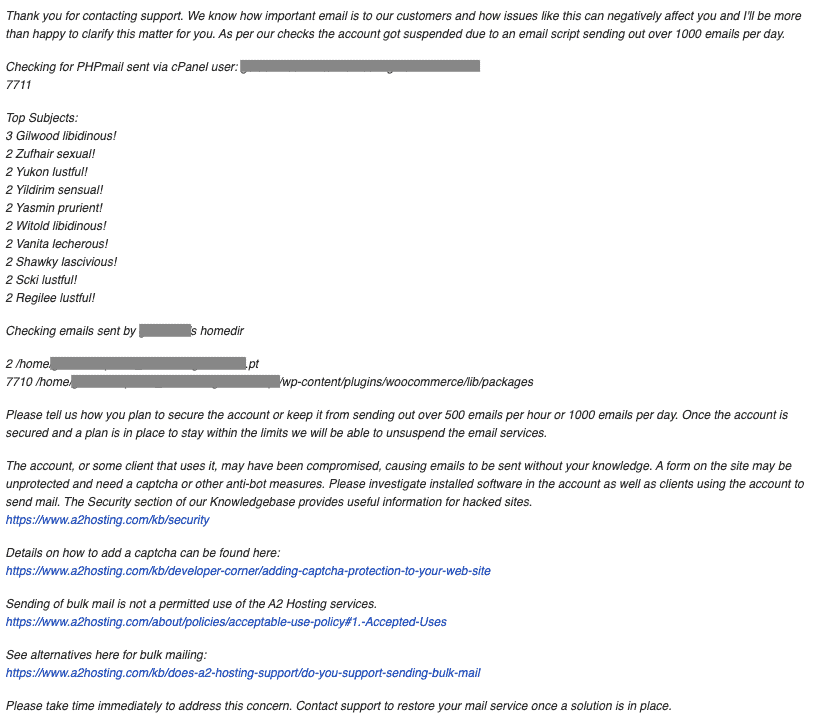
If WordPress is sending spam email, stop the unauthorized sending, then trace its source. The cause could be malware, stolen email credentials, or an abused form. A forged sender address can also make someone else’s spam look like yours.
Perhaps your host has blocked outgoing mail. Or a customer has forwarded a scam with your name on it. Either way, you need a fix that stops the spam without leaving customers stranded.
Start with the checks below. We’ll help you separate a hacked site from a mail problem, then deal with the right cause. If the evidence points to a compromise, review your WordPress security beyond the email issue too.
TL;DR: Ask your host or email provider to pause unauthorized sending and save a sample message with full headers. Scan the site, check connected mail accounts, and fix the source. Remove queued spam before sending resumes. If genuine emails are landing in junk, check delivery settings instead.
What kind of spam problem do you have?
Sending spam and having your emails marked as spam are different problems. Use what you’re seeing to choose where to start.
| What you see | Start here |
|---|---|
| Your host confirms unauthorized outgoing mail | Contain sending and trace its source |
| Strangers receive your form’s confirmation email | Check form auto-replies and recipient settings |
| Junk submissions arrive in your inbox | Add form spam protection |
| Expected receipts or password resets land in junk | Check email authentication and reputation |
| Bounces arrive for mail you never sent | Have the provider trace the original headers |
Bounces alone don’t prove a hack. Spammers can forge your sender address, sending delivery failures back to you.
An empty Sent folder doesn’t settle it either. Server scripts and email APIs can send without leaving a copy there.
Tip: Unsure which case fits? Save one original spam message and ask your host to trace it and then start a site scan while they investigate. You don’t have to guess before asking for help.
How to stop WordPress from sending spam emails
If unauthorized mail is leaving your site or account, follow these steps. If all the messages are yours, skip to the delivery section below.
1. Pause the sending and save the evidence
Ask your host or email provider to restrict the affected sending route. That might mean blocking a script, disabling a mailbox, or revoking a stolen API key.
Pause nonessential campaigns and abused auto-replies too. A broad mail block can stop order receipts and password resets, so check what else will be affected.
Before deleting files or clearing queues, keep:
- A sample message with full headers, plus any bounce notice.
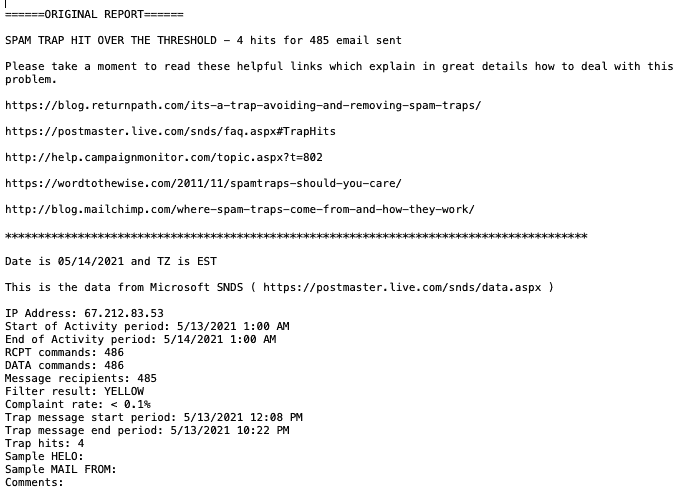
- The abuse alert, including message or queue IDs.
- The time you noticed the issue, with its timezone.
- Available logs and a site snapshot from before cleanup.
Label the snapshot as potentially infected and keep it private. It preserves the current state; it isn’t a clean backup to restore later.
Tip: A maintenance page may not stop mail. Scheduled tasks, server scripts, and stolen service credentials can keep working behind it. Ask the provider to contain the sending itself.
If your host has blocked mail, fix the cause before switching providers. Moving the same compromised setup can move the spam along with it.
2. Trace the message to its source
The From address isn’t proof of where an email came from. Match a sample message against the host’s or mail provider’s records.
Ask support to check these details where available:
| Detail | What it helps establish |
|---|---|
| Message ID and timestamp | Which sending event matches the complaint |
| Sending account, SMTP login, or API key | Which account authorized the send |
| Source IP | Where the sending connection came from |
| Script path or process | Whether website code generated the message |
Then follow the route the evidence points to.
The website generated the email
Check whether the timestamp matches a form submission, registration, campaign, or scheduled job. An abused feature can send unwanted mail even when the code itself is legitimate.
If there’s no valid explanation, scan the installation and ask your host to inspect the account.
An empty WordPress mail log doesn’t rule out malicious sending. Malware can send outside wp_mail(), bypassing the route your mail plugin records.
A mailbox or mail-service account sent it
Check recent logins, connected apps, SMTP credentials, and API activity. A stolen credential can let someone send mail without accessing WordPress.
Revoke the affected access and end unknown sessions. Check for changed recovery details and forwarding rules before reconnecting legitimate integrations.
The provider can’t find a matching sender
Ask them to check the original headers for spoofing and other sending paths. A spammer may have forged your address on mail sent elsewhere.
If spoofing is confirmed, cleaning WordPress won’t stop that sender. Review domain authentication and DMARC with your provider. Investigate any separate signs of site compromise too.
Tip: Send the original message, not a screenshot. Use “Show original,” “View source,” or your mail app’s export feature. Headers help trace the route. Share them privately; they can include personal details.
3. Scan the files and database
A site can look normal while a malicious script sends spam in the background. Loading the homepage isn’t a useful test for this kind of infection.
Use a scanner with access to the site’s files and database. A public URL scan can find exposed malicious content, but it can’t fully inspect private server files.
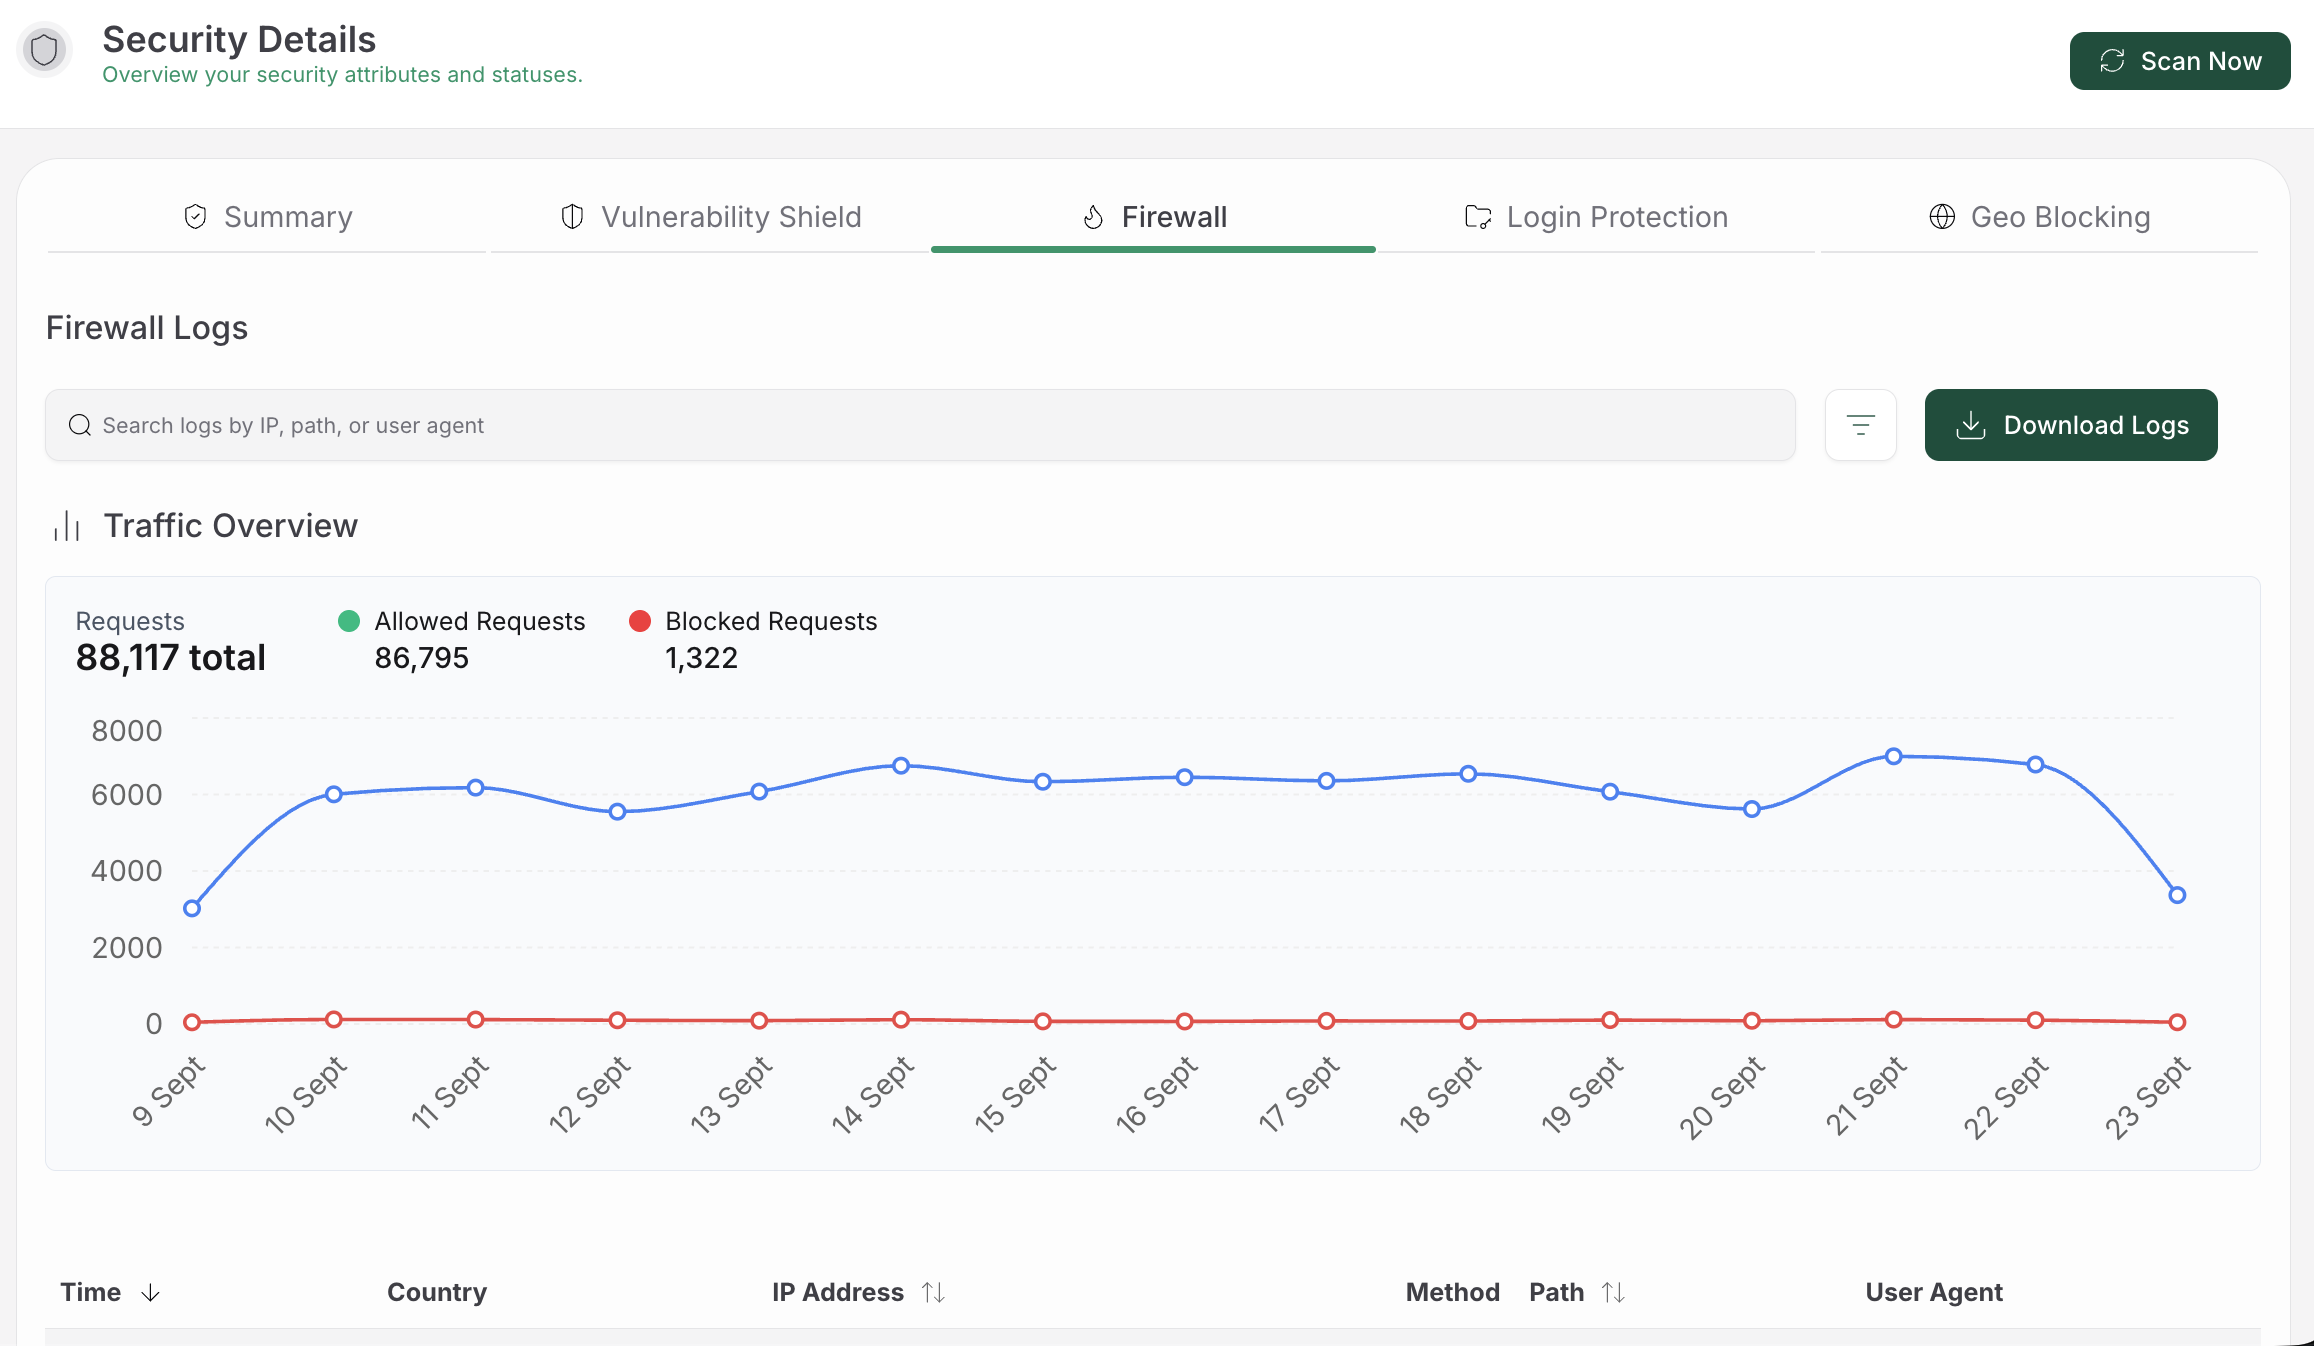
Our MalCare malware scanner checks WordPress files, plugins, themes, uploads, database content, and WordPress scheduled tasks. Connect to the affected site and run a full scan.
If the site is suspended, ask your host how to arrange cleanup access.
Review these alongside the scan:
- Administrator accounts: Can you account for each one?
- Mail settings: Have recipients or service credentials changed?
- Plugins and scheduled jobs: Did anything unfamiliar appear around the incident?
Don’t delete something based on its name alone. Custom code may be valid; a familiar file may contain an injection.
Tip: Still seeing unauthorized sends after a clean scan? Ask the host to check other sites in the account, server-level scheduled jobs, and mail accounts. A WordPress scan doesn’t cover the entire hosting environment.
4. Clean the infection and close its way back in
Removing one mailer file isn’t always a complete cleanup. A backdoor can let an attacker return and replace it.
Choose a recovery path that fits the evidence and the help available:
| Recovery path | What to check |
|---|---|
| Malware cleanup tool or security service | Scope of cleanup, remaining access, and follow-up checks |
| A known-clean backup | Whether it predates the compromise and preserves needed data |
| Manual cleanup by an experienced developer | Files, database, users, scheduled tasks, and custom code |
MalCare’s malware removal workflow backs up affected data, removes detected malware, and rescans the site. Cleanup covers files, database content, malicious scheduled tasks, and rogue administrator accounts.
Your host or mail provider still needs to handle abuse in its own systems, including queued spam.
For manual cleanup, compare code with trusted WordPress, plugin, and theme copies. Preserve valid custom changes, and check database content and accounts as well as files.
Don’t delete code just because it uses base64_decode() or another function on a malware checklist. Those functions have valid uses. What the code does matters more than a keyword match.
After cleanup or restoration, patch the vulnerable software or remove it if no supported fix exists. Remove pirated extensions and unused software too.
Tip: Restore from before the compromise, not just before the complaint. The attacker may have arrived days earlier. Scan the recovery copy and close the original entry point. On a store, plan how to preserve newer orders before restoring.
5. Revoke stolen access and review the mail queue
Revoke known-compromised credentials as soon as you identify them. Once the site is clean, replace other credentials that may have been exposed, using a trusted device.
Check the relevant accounts and access:
- WordPress: Admin passwords, unknown users, application passwords, and active sessions.
- Hosting: Control-panel, SFTP, and SSH access.
- Database: Credentials exposed through the compromised site.
- Email services: SMTP passwords, API keys, and connected apps.
Update saved connection details when changing passwords. A new database password, for instance, must also be reflected in the site’s configuration.
Reset WordPress security keys and salts to invalidate login cookies. Enable two-factor authentication where supported, and check your own device if you suspect it was compromised.
Next, ask the provider to inspect the mail queue: messages waiting to leave.
Queued spam can keep sending after the website is clean. Have confirmed spam removed, while preserving genuine mail where possible. Don’t blindly purge waiting order receipts or password resets.
Tip: “MTA queue is too large” means there’s a backlog. The mail transfer agent handles email on the server. Spam can fill its queue, but so can delivery failures or a legitimate volume spike. Ask what is waiting and why.
6. Restore sending and test the emails that matter
Ask your provider what it needs before lifting restrictions. Share the cleanup result and the steps taken to close the source of abuse.
Check both sides of recovery: spam has stopped, and legitimate mail works.
| Test | What to confirm |
|---|---|
| Password reset | The intended account receives a working reset email |
| Contact enquiry | The team receives it and replies behave as expected |
| Order notification | The expected store emails reach their recipients |
| Sending records | No new unauthorized messages or unexplained bursts |
| Follow-up scan | No remaining detected infection |
Review activity after sending resumes, including the next scheduled sending cycle. One quiet hour doesn’t establish that a recurring job has stopped.
Legitimate mail still gets blocked?
Ask your provider to check the actual outgoing mail IP and sending domain. The mail IP may differ from your website’s IP.
Resolve relevant blocklist or reputation issues after stopping the abuse. Removal from one list doesn’t guarantee inbox delivery elsewhere.
Customers received a scam?
Use a trusted channel to identify the message they should ignore. Give specific next steps if they entered a password or payment details.
Stick to confirmed facts. Don’t claim customer data was stolen—or untouched—without evidence.
Your genuine emails land in spam? Check delivery instead
An expected email in the junk folder isn’t proof of malware. If you recognize the recipients, messages, and sending activity, start with authentication and reputation.
Check SPF, DKIM, and DMARC
Your email provider should supply the DNS records for its service.
| Record | What it checks |
|---|---|
| SPF | Whether the sending server is authorized for the envelope-sender domain |
| DKIM | Whether the message has a valid domain signature |
| DMARC | Whether a passing SPF or DKIM result uses a domain matching the visible From domain, under its rules |
Use your provider’s values, and have existing records reviewed before adding new ones. A strict DMARC policy can block legitimate services if you haven’t accounted for them.
For personal Gmail accounts, Google’s sender guidelines require SPF or DKIM for all senders. Bulk senders need SPF, DKIM, and DMARC, plus further requirements such as one-click unsubscribe for marketing and subscribed mail.
Use an authenticated service, then check reputation
An SMTP or email API plugin can route WordPress mail through your chosen provider. It improves the sending setup; it doesn’t remove malware.
Authentication also doesn’t guarantee inbox delivery. Complaints, unwanted campaigns, sending history, and shared-IP reputation can affect filtering.
Send campaigns to people who agreed to receive them, and make unsubscribing easy. Ask the provider to investigate rejections using the actual response codes.
Tip: Use your own address in a form’s From field. Put the visitor’s address in Reply-To. Sending as a domain you don’t control can cause authentication failures. Check your form plugin’s instructions.
A useful troubleshooting detail: the WordPress mail reference says a successful wp_mail() result means the request was processed. It doesn’t prove the recipient received the email. Check delivery records too.
Is a contact form sending the spam?
A form can be abused without the site being hacked. Check its submissions and notification settings to see whether they match the unwanted emails.
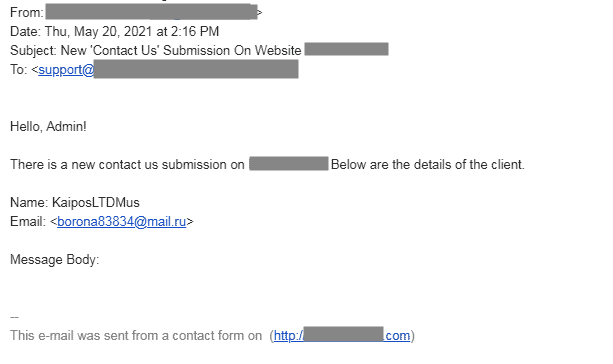
There are two common situations:
- Junk reaches your inbox. Bots are submitting spam to the form.
- Strangers receive confirmations. Bots may be entering other people’s addresses to trigger auto-replies.
That second case is easy to miss. If a reply repeats the visitor’s message, the form can forward the bot’s spam with your branding.
Contact Form 7’s configuration guidance warns about user-supplied addresses in To, Cc, and Bcc. Review those fields in whichever form tool you use.
Fix the form, then test a real enquiry
- Pause the abused auto-reply. Stop it sending while you investigate.
- Check recipients. Keep team notifications addressed to your team; review visitor confirmation settings.
- Remove untrusted content from visitor replies. Don’t echo submitted spam back out.
- Add supported protection. Use server-side spam filtering, submission limits, and bot checks such as Turnstile or reCAPTCHA where available.
- Submit a genuine enquiry. Confirm that real messages arrive and replies go to the right place.
If mail keeps going out independently of form submissions, return to the site and account checks. Form spam and malware can occur together.
Keep the spam from coming back
Focus on the control that would have stopped this incident, then maintain the basics:
- Patch supported software. Remove abandoned or unused extensions.
- Limit admin access. Use unique passwords and two-factor authentication.
- Keep scans and backups running. Use a WordPress security plugin to scan for malware regularly, and test that your backups can restore.
- Watch sending volume and spend. Investigate unexpected bursts early.
- Use a firewall. It can reduce malicious requests, but doesn’t replace cleanup or credential revocation.
If a form caused the abuse, fix the form. If a stolen key caused it, secure the systems holding that key. A lasting fix addresses how these messages were sent.
FAQs
Why is WordPress sending spam email?
Malware, stolen mail credentials, or abused sending features can cause it. Someone can also forge your address without using your site. Match a sample message to provider logs to confirm the source.
How do I stop WordPress from sending spam emails immediately?
Ask your host or email provider to restrict the affected sending route. Pause abused forms or campaigns and revoke known-compromised access. Save evidence, then fix the source before restoring normal sending.
Will an SMTP plugin fix WordPress spam emails?
No. It won’t clean malware or cancel an attacker’s access. SMTP helps route legitimate mail through a provider. Fix a compromised site or account before connecting a new sending service.
Why do I get bounces for emails I didn’t send?
Your address may be forged, or someone may be sending through a connected account or script. Ask the provider to trace full headers. The From address and Sent folder alone can’t establish what happened.
Can restoring a backup fix a spam-email hack?
Yes, if the backup is clean and you close the original access path. Preserve newer content where needed and scan the restored site. A restore won’t revoke stolen mail credentials or clear the provider’s spam queue.
Before you switch sending back on
Confirm the source has been fixed, compromised access is revoked, and queued spam is handled. Then test the emails your customers need.
The goal is simple: unwanted messages stop, and legitimate messages get through. Verify both before calling the problem solved.