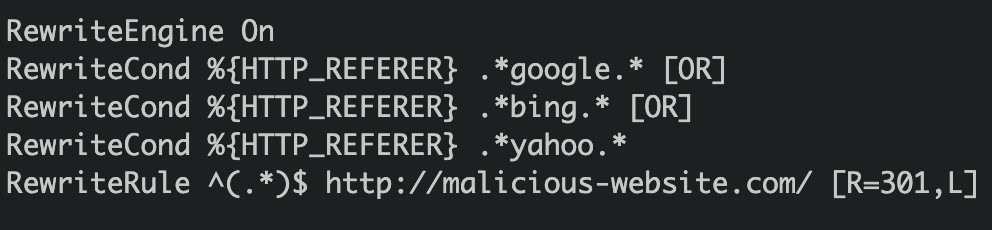
If you find a strange .htaccess file, notice visitors being redirected to an unrelated site, or see the file return after deletion, your site may have WordPress .htaccess malware. Because this file controls how Apache handles website requests, attackers can use it to redirect visitors, block access, or hide other malicious activity.
Deleting the file may remove the visible symptom without fixing the infection.
The malware may have changed other WordPress files, added unauthorized users, or compromised your hosting account. This guide explains how to preserve the evidence, investigate the wider site, restore trusted rules, and verify that the malware is gone.
TL;DR: Preserve the current .htaccess file and make a rollback copy before changing it, because it may show how the attack is working. Do not keep deleting or regenerating the file in isolation: scan and clean the full site, find what is rewriting it, restore only known-good rules, verify the site, and rotate affected credentials.
What is WordPress .htaccess malware?
.htaccess malware is malicious Apache configuration placed in a directory-level configuration file on a WordPress site. Apache reads the file while handling requests, so an attacker can use it to redirect visitors, serve spam, deny access, alter error pages, or show different content to search engines and normal visitors.

The file itself is normally legitimate. WordPress commonly uses a root .htaccess file to support pretty permalinks, or human-readable post and page URLs. Plugins, hosting tools, security rules, redirects, and other applications can also add valid instructions. A hidden file or an unfamiliar rule is therefore not proof of infection by itself.
The more useful question is not, “Does this file look normal?” It is, “What is this file supposed to do on this site, and what is writing to it?” A suspicious file does not prove that it was the first or only point of entry.
Signs of .htaccess infection
The strongest reason to investigate .htaccess and the wider site is a combination of unexplained behavior and unexpected file changes. Look for these clues:
- Visitors are sent to an unrelated page, especially after coming from a search engine or another site.
- Search results show spam or pages that are not visible during an ordinary visit.
- The site returns a 403 Forbidden or 500 Internal Server Error after a file change.
- A new rule changes access to a folder, file type, login page, or error page without an explanation.
- The file contains redirects, rules that check the visitor’s browser or where they came from, or instructions that do not match anything the site owner installed.
- .htaccess, index.php, or another file changes back after it was repaired.
- Only some visitors see the problem, or the problem appears only on a particular URL.
These symptoms are clues, not a diagnosis. Caching, a bad redirect, a plugin rule, a host-level configuration, a syntax error, or a server-version mismatch can produce similar behavior. As part of a broader WordPress security audit, compare the current file with a known-good copy and test from more than one browser or network before calling a rule malicious.
Directly opening the homepage is a weak test because malicious rules can behave differently for search referrals, crawlers, logged-in administrators, mobile devices, or error requests.
Check the server before changing the file
First establish whether the server can read .htaccess. The file is used by Apache and servers such as LiteSpeed that support Apache-style configuration. LiteSpeed may support it with its own limits and configuration. An Nginx-only site generally does not read .htaccess at all. A managed host may hide the real server configuration or apply rules outside the WordPress directory.
This matters when a rule appears to have no effect. The cause may be Nginx, a host setting that disables directory rules, the wrong directory, a cache, host policy, or an instruction the server does not support. A 500 response after a change can mean invalid syntax, an unavailable module, or a directive that does not match the server version.
📝 Note: If your site runs Nginx, Apache-specific assumptions may not apply. Confirm the server stack with your host before changing .htaccess.
Also identify the WordPress installation directory. A root file may affect the directories below it, while a file in a child directory may affect fewer locations. A subdirectory installation can have a different location and rewrite setup. If several sites share one hosting account, inspect the account boundary as well as the individual WordPress directory.
What to do before editing .htaccess
Treat the current file as evidence until you understand the incident.
- Save an untouched copy outside the public web directory. Record when you found it, what URL or error exposed the problem, and whether the behavior changes for logged-in and logged-out visitors.
- Create a separate working copy for inspection. Do not rely on a screenshot when exact text and ordering matter.
- Avoid opening an unfamiliar redirect destination. Use a safe device or an isolated browser session if you need to confirm what visitors see.
- Ask the host about temporary isolation if the site is actively harmful. Do not delete every .htaccess file across the account or other sites.
- Preserve a known-good backup if one exists. Check its date and which files it includes, because a backup made after the site was compromised may preserve the attacker’s files.
📝 Note: Do not run a broad recursive delete. Parent and child directories can have legitimate rules, and other applications in the account may depend on them. Deleting the visible file does not remove the code, scheduled task, account, or access path that can recreate it.
A safe way to clean a suspicious file
The safest fix is a controlled recovery, not a file-only reset.
1. Establish what the clean configuration should be
Compare the file with a known-good backup, the rules generated for the current WordPress installation, and documented rules added by the host or trusted plugins. Check whether a parent file also applies.
Keep in mind not to copy a large hardening snippet from an unrelated site. Apache modules, server versions, directory permissions, and application paths differ. An instruction that is valid on one host can cause a 500 error or lock the owner out on another.
WordPress can regenerate its basic rewrite rules when the administrator opens Settings > Permalinks and saves the settings. This can restore ordinary permalink handling, but it is not malware removal. It may remove custom redirects or security rules, and it does not clean PHP files, plugins, themes, uploads, the database, users, scheduled tasks, or the hosting account. Preserve custom rules before using this step.
📝 Note: Use WordPress’s official Apache guidance as the reference for standard rules. Treat copied snippets as host-specific configuration, not as a universal cleanup method.
2. Scan and clean the complete installation
Inspect core files, plugins, themes, uploads, database content, administrator accounts, scheduled tasks, and server logs. Look for changes in more than one file and for new accounts or access keys. If multiple sites share the hosting account, consider whether the same process could affect them too.
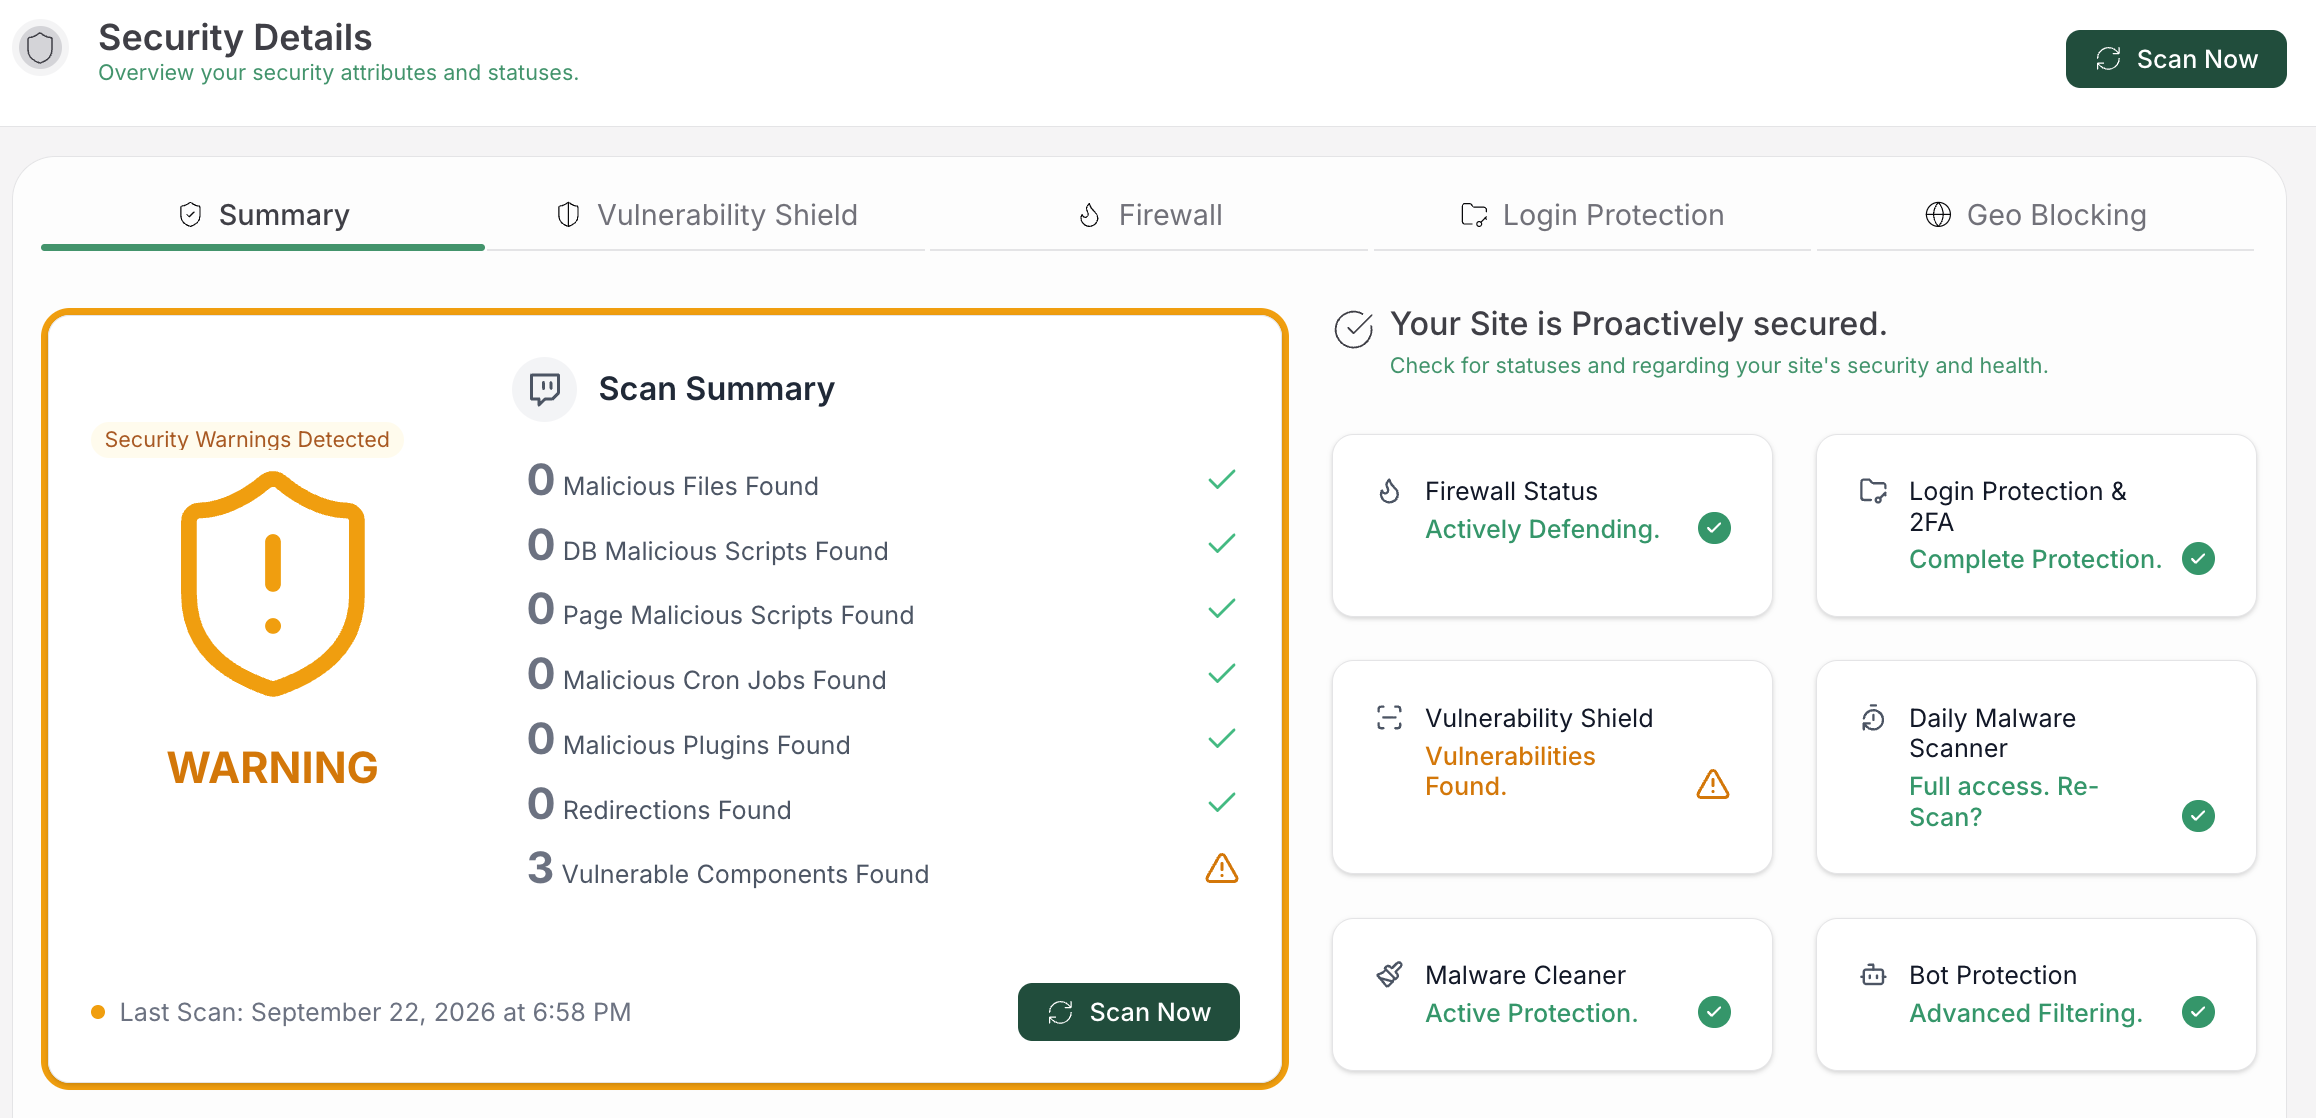
The goal is to find the writer- if hidden code that gives an attacker access, or a compromised administrator, can still write files, replacing .htaccess only removes one visible symptom. A scanner can help identify suspicious files and database content across the WordPress installation.
If the file returns after a controlled replacement, stop treating the event as an isolated configuration problem. Capture the time of the rewrite, compare other changed files, inspect scheduled tasks and unknown users, and ask the host to review account and access logs. Repeated reinfection is evidence that the code or task that keeps rewriting the file has not been removed, even if the new .htaccess file looks correct for a short time.
3. Restore and test in a controlled order
After the wider investigation, restore the known-good rules or regenerate the basic WordPress rules. Then test the site from the outside, not only while logged in:
- Open the homepage and several affected URLs in a private session.
- Confirm that the expected response status, such as 200, 403, or 500, is returned and that there is no unexpected redirect.
- Test a post, page, media URL, login page, and a URL that previously failed.
- Recheck the file after waiting long enough for scheduled tasks and caches to run.
- Confirm that custom redirects, security rules, forms, and important integrations still work.
Keep the old copy until the checks are complete. A successful homepage load is not enough: a malicious rule can target one directory, one visitor group, or only a missing page.
4. Rotate access after cleanup
Change WordPress administrator passwords, hosting and control-panel passwords, file-transfer or server-login credentials such as SFTP or SSH, database credentials, API keys, and any other secrets that may have been exposed.Remove unknown users and keys, review WordPress user accounts and administrator roles, and update WordPress, plugins, and themes from trusted sources.
Use unique passwords and accounts with only the access they need. Keep tested backups, restrict dashboard file editing where appropriate, and separate unrelated sites when the host supports it. These steps reduce the chance of reinfection, but they do not prove that existing malware is gone. Prevention starts after the current incident has been contained and checked.
Why does .htaccess malware keep coming back?
.htaccess malware keeps coming back because something that still has access is rewriting it. Common possibilities include an infected plugin or theme, modified core files, hidden PHP code that gives an attacker access in uploads, a compromised administrator or hosting account, a scheduled WordPress task, a server-level process, or another site sharing the account.
The source may be adjacent to the file rather than inside the WordPress installation. A parent-directory rule or another compromised site can affect a shared directory. Repeated file changes should therefore trigger an investigation across the hosting account, not another blind deletion.
A permission change can also make the file harder to edit, but it does not remove the process or account that made the change. Use permissions as one containment measure only, and verify that the application still has the access it needs after cleanup.
Can I just delete .htaccess?
Usually, no. Deleting it may remove a redirect or restore access temporarily, but it can break permalinks, remove legitimate security or redirect rules, destroy evidence, and leave the writer in place. It is safer to preserve the original, determine the expected rules, investigate the full site, and replace the file in a controlled way.
If the file is causing an active harmful redirect and you need immediate containment, use a saved copy and coordinate with the host or a qualified administrator. Do not assume that a missing file means the incident is over.
How to prevent another .htaccess incident
Once the site is clean and verified, reduce the chance of another incident:
- Keep WordPress, plugins, themes, and server software updated.
- Remove software and administrator accounts that are no longer needed.
- Use unique credentials and accounts with only the access they need for WordPress, hosting, file transfer, server login, and databases.
- Maintain backups that are separate from the live hosting account and test restoration.
- Monitor unexpected file changes, new users, scheduled tasks, redirects, and search spam.
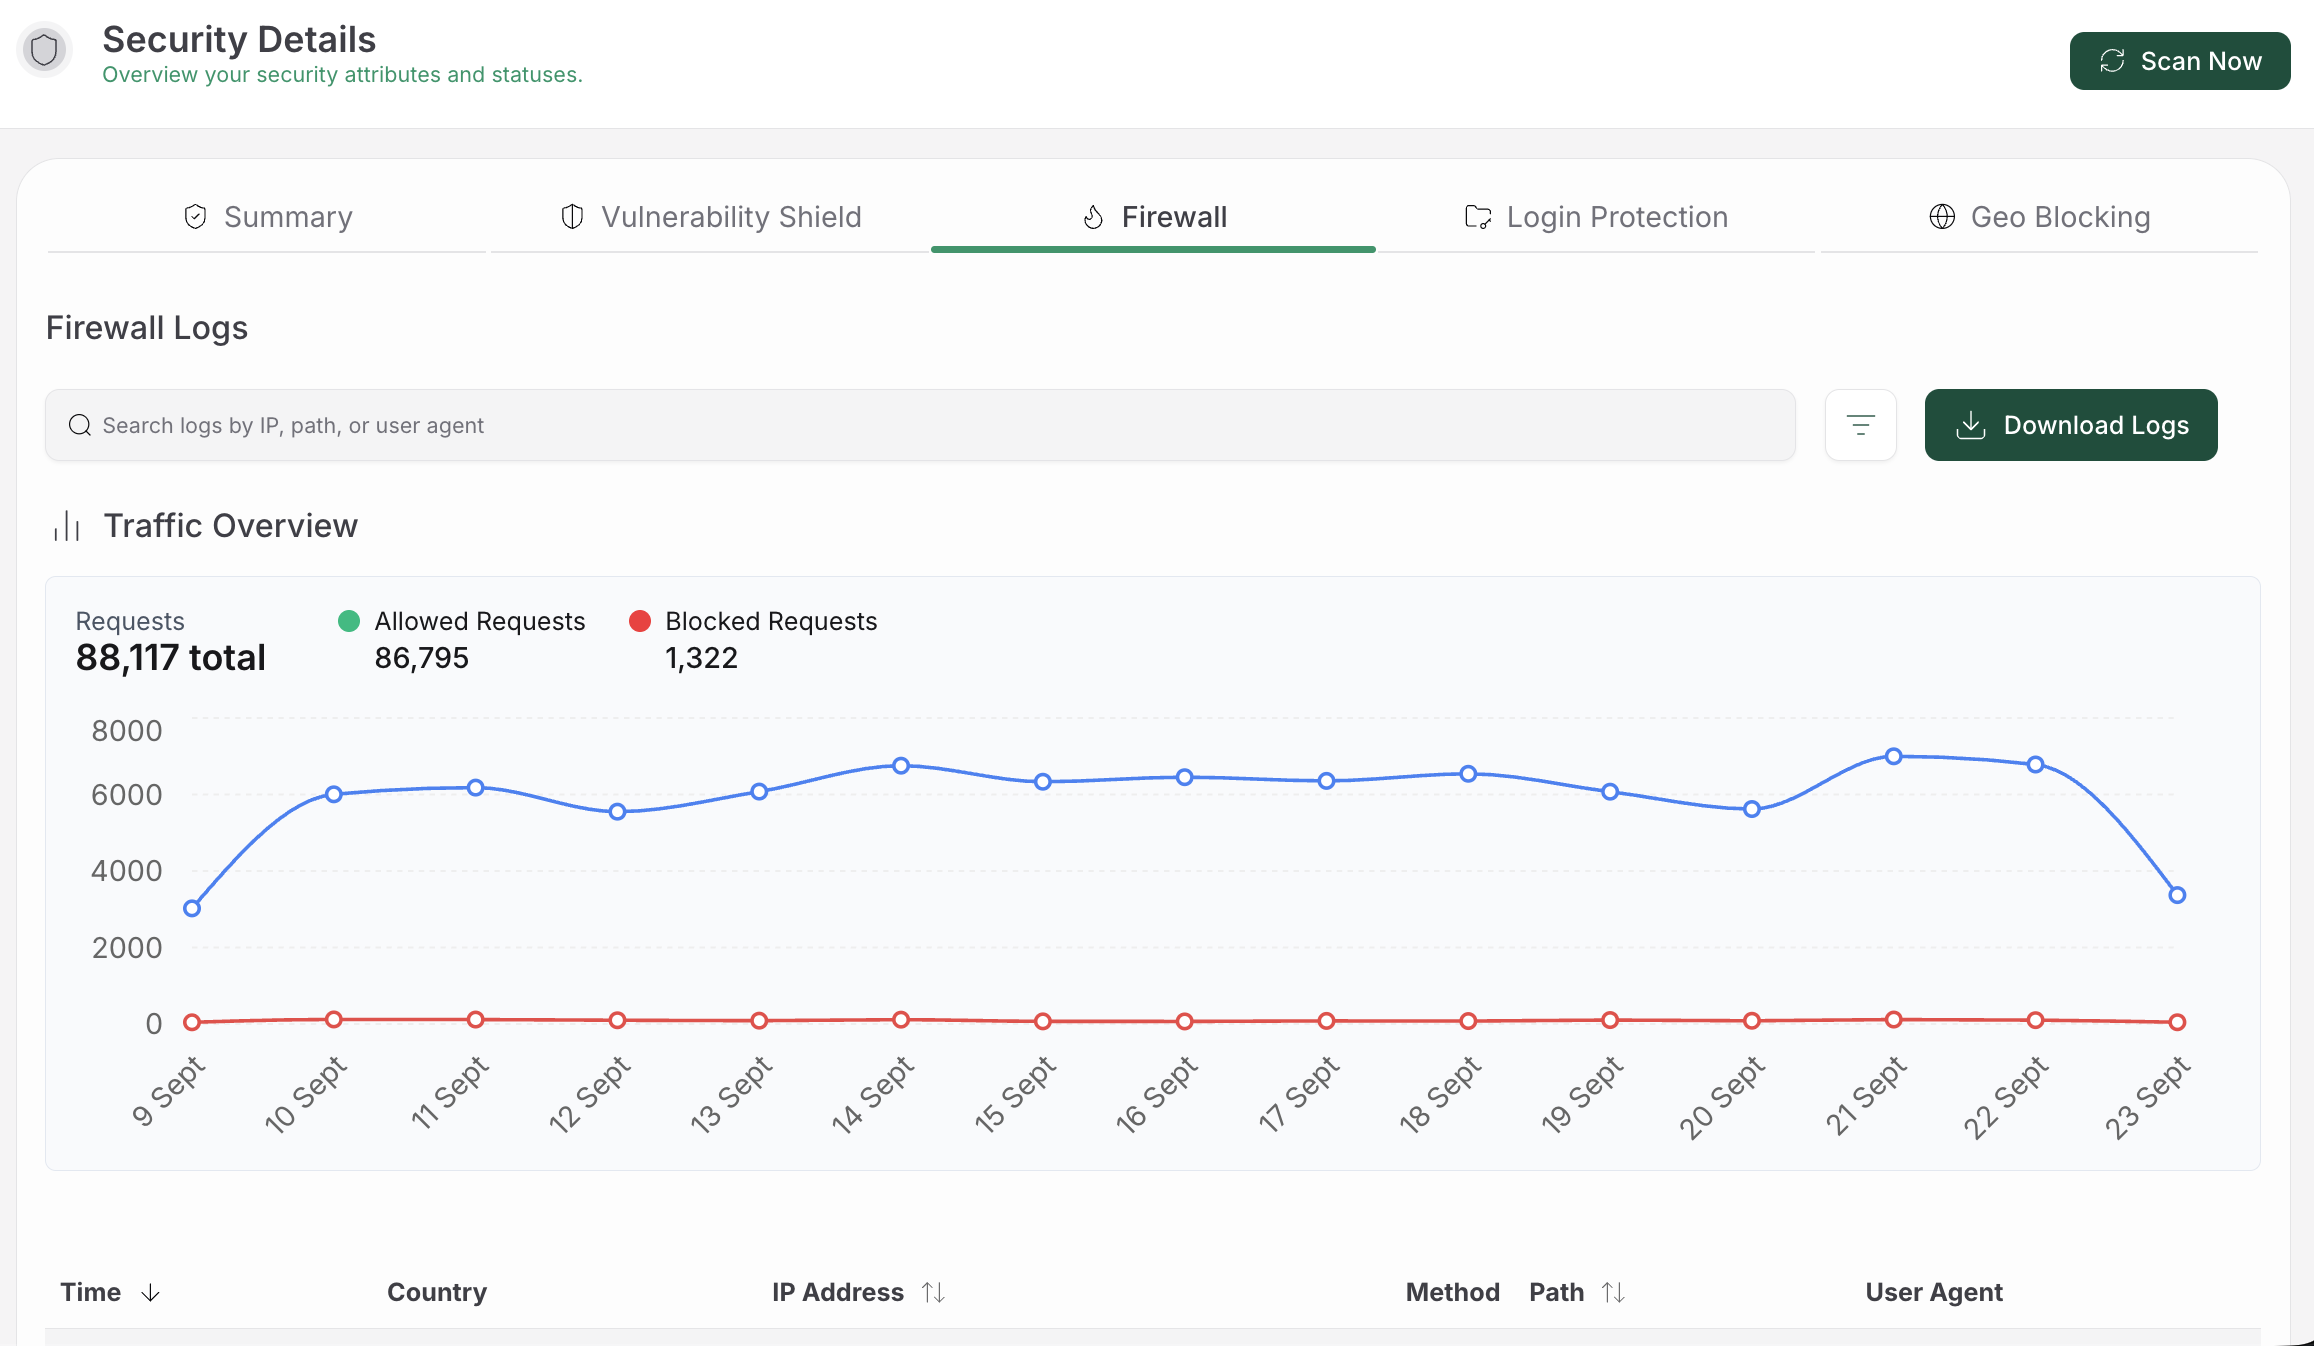
- Use a WordPress firewall to block malicious traffic, and choose a security plugin that combines scanning, cleanup, and protection.
- Follow safe .htaccess hardening practices instead of pasting rules from an unrelated server configuration.
- Separate unrelated sites where possible so one compromised site cannot become an easy path to another.
- Keep a record of intentional .htaccess changes and the plugin or host that made them.
These controls make unusual changes easier to spot and reduce the ways an attacker can return. They are not a substitute for cleaning the existing installation and rotating compromised credentials.
FAQs
What is the safest first step when .htaccess looks infected?
Save an untouched copy outside the public web directory, record the symptom, and avoid repeatedly deleting the file. The copy preserves evidence while you determine the expected rules and investigate the wider installation.
How can I recreate the WordPress .htaccess file?
After preserving the old file and checking for custom rules, open Settings > Permalinks in WordPress and save the settings. This can restore basic rewrite rules, but it does not remove malware from the site, database, users, scheduled tasks, or hosting account.
Does every WordPress site use .htaccess?
No. Apache and some servers that support Apache-style configuration use it, while an Nginx-only site generally does not. LiteSpeed, managed hosting, server settings, caching, and the directories affected can change how the file behaves.
Why does .htaccess become infected again after I fix it?
Another file, scheduled task, administrator, hosting account, adjacent site, or server-level process may still have write access. Repeated recreation means you need to look for whatever keeps rewriting the file across the full site and account instead of replacing it again.
When should I ask for professional WordPress malware cleanup?
Ask for help when the file returns, several sites are affected, you find unknown administrators or database changes, you cannot contain an active redirect, or you lack safe access to the files, logs, or hosting account. A broader cleanup can then address the site and account rather than only the visible configuration file.
Conclusion
.htaccess is often the part of a WordPress compromise that a site owner can see, not the part that started it. Preserve the file, identify the server and expected rules, investigate what can write to it, and verify the complete site after recovery.
If the file keeps returning or the incident reaches other sites, users, or the hosting account, stop treating it as a one-file problem. Contain the site, get qualified help when needed, and rotate exposed access after the wider cleanup is complete.