We have fixed a bug in how the MalCare plugin handles a rare invalid request. We haven’t seen it being abused, but it was possible, so we have closed it.
What changed in this security update
If you’re a MalCare customer, please rest assured that you’re already protected.
In short: a request with a specific malformed parameter could make the plugin do a lot more work than it should, so someone hammering that endpoint could put extra load on a site’s server.
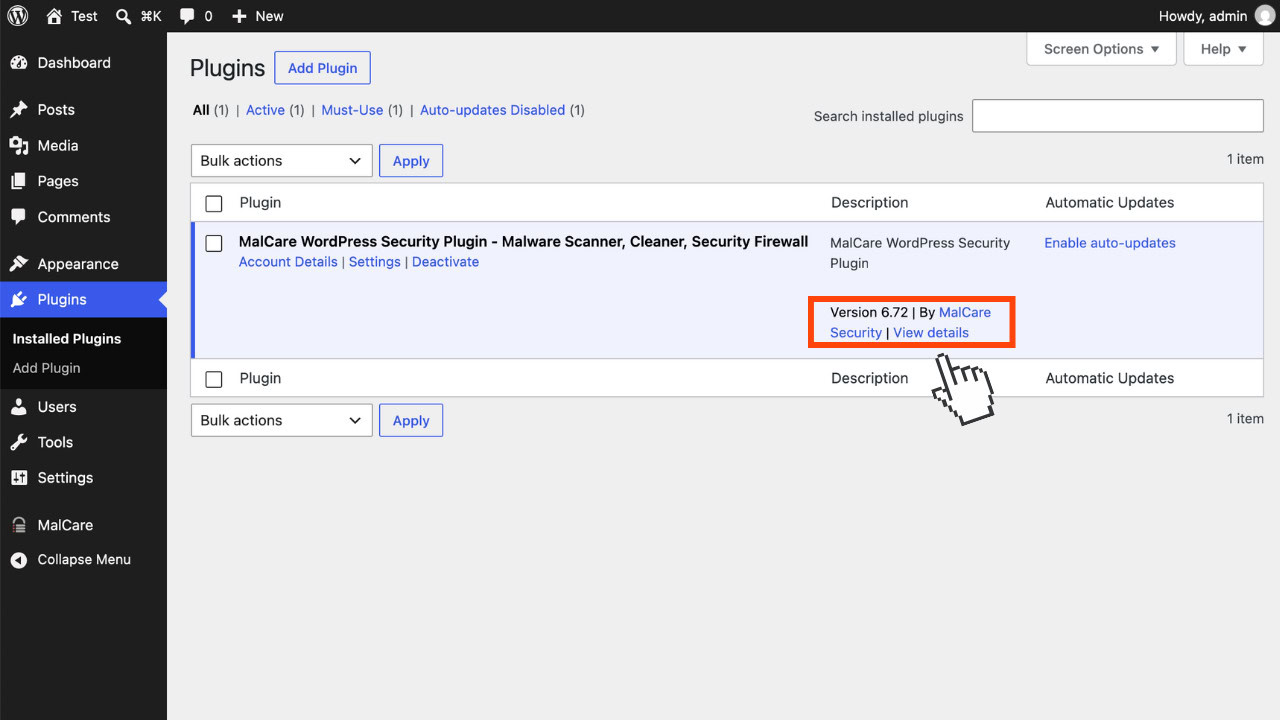
As soon as we found this, we tightened the parameter checks and automatically updated them across all customer sites. To confirm, you can check that your site is running MalCare v6.72.
We’ve also checked the surrounding code for similar cases and added stronger safeguards there as well. We thank Ananda Dhakal from Patchstack for identifying the issue and working with us on the fix.
If you have any questions or concerns, our support team is here to help.